Monday, July 07, 2008

Nuwar Looks for News Readers?

What news headlines would make you click an email link, even though you KNOW you aren't supposed to do that? The authors of the newest round of Nuwar, which may or may not be the same "storm" worm that we've seen two rounds of already this month, think they know.

Based on a review of this afternoon's "infect you through news headlines", the virus authors believe you want to know about Obama, McCain, Angelina Jolie, and the new Batman movie.

The spam for malware-infection "PornTube" sites is really out of control lately.

The current trend is to hack into someone's site, leave an "r.html" file there, and then send spam with totally unrelated subjects which, when clicked on, will open very offensive porn images and also try to infect the visitor by sending them to a secret website through an "iFrame". (The iFrame redirection site, digitaltreath.info, is now down and will hopefully stay down, after nearly a month of hosting badness.)

The malware which is present on each site is a file called "video.exe", which at least several AV products (AVG, McAfee, Microsoft, Trend) are calling "Nuwar", aka Storm.

Symantec calls it "Trojan.Erotpics", while several others call it "Exchanger" (AhnLab, BitDefender, ClamAV, Fortinet, VBA).

eSafe, F-Prot, Panda haven't weighed in yet -- VirusTotal shows 22 of 33 detections right now.

The template seems to be, pick a random subject, pick a random body line, pick a random website, with the choices I've seen today including:

Subjects
===========

  • Actors required Sign up now
  • Angelina jolie shock pregnancy discovery
  • Angelina Jolie suffers miscarriage
  • Apple files for bankruptcy
  • Are you getting enough
  • Beyonce breaks up with Jay Z
  • Blast in Pakistan
  • Brad Pitt confesses to betrayal
  • China fires missle in Taiwan's direction
  • Christopher Nolan's Knight vision
  • Clinton withdraws support for Obama
  • Eminem found dead in disco toilet
  • Fantastic year for spanish athletes
  • Federer crashes out
  • Fight for your benefits and rights
  • Heath Ledger never saw the Dark Knight
  • Hurricane hits Caribbean islands
  • India plans attack on terrorists
  • Join our talent hunt contest
  • Latest gossips on celebrities
  • Madonna admits to extra marital affair
  • McCain suffers heart attack
  • McCain withdraws from presidential race
  • McCaine vows to remain celibate
  • Memorabilia for heroes only
  • Miley cyrus naked photos expose
  • Obtain your degree in six months
  • Oil falls below $100 a barrel
  • Party scenes with American idols
  • Retire a millionaire
  • Search for singing talents
  • Spielberg found dead in freak accident
  • Take a look only if you are worth it
  • The Mummy 3 movie bankrupt, release delayed


Bodies
===========

  • A-rod admits to previous secret gay fetish
  • Asian girls mass Org partying
  • Barack Obama has been exposed to lack patriotism and shows loss of support from the masses
  • Can you take on two hot girls
  • Check out your popularity polls among colleagues
  • Elton John’s new lover
  • European girls group Org scenes
  • FBI surveillance team reveals trade secrets
  • French hospital in the south of France has admitted Hollywood actress Angelina Jolie
  • Fully online Master's degrees available at accessible prices
  • Gays in U.S military
  • Gun ban threatens to destroy obama's campaign
  • J Lo secret marriage threatens to destroy current marriage
  • John McCain gathers support from lackeys in Iraq and Afghanistan towards his election campaign
  • Kobe Bryant traded to Toronto in latest blockbuster trade
  • Late and great Ledger in running for posthumous Oscar award
  • Lindsay lohan drugged out at own birthday party
  • Madonna split finalized, Guy Ritchie in tears
  • ndia vows to find the masterminds behind the suicide attack that have killed entire embassy staff in Afghanistan
  • Obama belittles McCain's ability to be a presidential candidate contender at his age
  • Obama openly supports abortion and gay rights in bid to win more support from the masses
  • Oprah Winfrey announces wedding plans
  • Paris Hilton in new naked pictures romp at 4th of july party
  • Places to go for secret rendezvous
  • Pregnant Angelina Jolie asked the media to leave her alone while she waits to give birth to twins
  • President Bush latest political guffaw
  • Rating of stolen car for 2007
  • Republican John McCain admits he has no ideas how to jump start the economy and that the Democrat's stimulus plan is the way to go
  • Senator McCain found unconscious in toilet
  • Start your own business and make more money
  • The sky is the limit for Christian Bale as he returns for a second attempt at taming Gotham City
  • This week top travel destination
  • Videos of your neighbors making things
  • Videos on sports celebs and their flings
  • Wesley Clark snubs McCain's service as forgettable in July 4 tribute to the nation
  • Your colleagues are earning more than you


Websites
===========
PLEASE DO NOT VISIT THESE LINKS! THEY *WILL* ATTEMPT TO INFECT YOUR COMPUTER!!!!
Note, all of these sites may contain legitimate business on other pages, but these "r.html" pages have been placed on these domains by a hacker. We aren't saying these sites are guilty of anything other than having bad security.

http://209.222.133.85/r.html
http://50percentoff.nl/r.html
http://adlerautomobile.bg/r.html
http://avellanas.org/r.html
http://balcondelrio.com/r.html
http://boeckinggmbh.de/r.html
http://bursabil-net.com/r.html
http://www.cochesdeimportacion.formulacoches.com/r.html
http://chromet.com/r.html
http://www.dicon.eu/r.html
http://dysank.pl/r.html
http://ethereal-hell.telefragged.com/r.html
http://fabricadsonhos.com/r.html
http://fazemos.com.br/r.html
http://www.govdeli.com/r.html
http://houtkoning.nl/r.html
http://i-manager.it/r.html
http://iconn.pl/r.html
http://livresedotabaco.com/r.html
http://lpplegnica.pl/r.html
http://mediahits.de/r.html
http://phoenixadministration.com/r.html
http://pikous.fr/r.html
http://point1.angies-cafe.de/r.html
http://www.rundegg.com/r.html
http://s229782982.mialojamiento.es/r.html
http://savons-de-provence.com/r.html
http://superhostsite.com/r.html
http://testing.vuenosairez.com/r.html
http://www.trivium.hu/r.html
http://www.rundegg.com/r.html
http://zonamediabus.net/r.html


There seem to be at least two "active" sets of templates (so, you would never see "Angelina Jolie" subjects with the "Kobe Bryant" body, because they are in different template sets, as an example.)

So, news readers, beware . . .

Thursday, July 03, 2008

Storm Worm Salutes Our Nation on the 4th!

I had just left for my holiday weekend when one of our UAB Computer & Information Sciences students
called to let me know he thought he had a new Storm version on his hands.

He had received an email wishing him a happy Fourth of July, followed by an IP address, which he recognized as a traditional Storm-style email.

I ran a quick check in the UAB Spam Data Mine, and here is what we had so far (the oldest of these is around 90 minutes ago, so we'll have a fuller picture tomorrow I'm sure.)

Subjects
=================
Amazing firework 2008
America the Beautiful
American Independence Day
Bright and joyful Fourth of July
Celebrate Independence
Celebrating Fourth of July
Celebrating the Glory of our Nation
Celebrating the spirit of our Country
Celebrations have already begun
Fabulous Independence Day firework
God bless America
Happy Birthday, America!
Happy Independence Day
Happy Independence Day!!
Independence Day firework broke all records *
Spectacular fireworks show
Stars and Strips forever
The best of 4th of July Salute
Time for Fireworks
Wish your friends a happy Independence Day


Bodies
=================
Amazing Independence Day show
America the Beautiful
Celebrating the Glory of our Nation
God bless America
Sparkling Celebration of Independence Day
Stars and Strips forever
Super 4th!
The best firework you've ever seen

IP Addresses
=================
4.248.91.239
12.173.3.17
24.13.166.252
24.130.139.182
24.249.135.214
24.33.244.139
24.99.230.65
64.252.164.229
65.185.105.8
65.185.32.14
67.176.18.50
67.185.246.151
67.191.111.202
67.36.178.103
67.38.31.104
68.179.134.99
68.62.190.121
69.0.75.77
69.141.230.19
69.225.5.209
216.137.135.74
216.255.59.26


The website, which seems to invite visitors to play a fireworks video,
actually downloads the Storm malware in the form
of an executable called "fireworks.exe".


Detection is fairly good already, with 16 of 28 AV engines detecting at
VirusTotal.com, with each calling it the various well known names for Storm:

Dorf:
Sophos = "Troj/Dorf-BP"

Nuwar:
AVG = I-Worm/Nuwar.U
McAfee = W32/Nuwar@MM
Microsoft = Backdoor:Win32/Nuwar.gen!D
NOD32v2 = Win32/Nuwar.DC

Peacomm:
Symantec = Trojan.Peacomm.D

Peed:
BitDefender = Trojan.Peed.JLV

Tibs:
VirusBuster = Trojan.Tibs.AMZ

Zhelatin:
AntiVir = WORM/Zhelatin.Gen
GData = Email-Worm.Win32.Zhelatin.add
Kaspersky = Email-Worm.Win32.Zhelatin.add
Webwasher = Worm.Zhelatin.Gen


Because this is a holiday weekend, there may be quite a few people who don't get blocking in place right away.

Best of luck to you all, and to those who are fortunate enough to live in the United States of America, Happy Independence Day!

Wednesday, July 02, 2008

7-11 ATM Hackers (?) - More details

More details are now available about a trio of hackers who were indicted back in March on charges of stealing more than $5M from customers of ATMs. In a July 1st USA Today story few facts were revealed, but it was enough to spin the story back up in the media. I'm getting enough questions about it, I thought I would try to summarize what we know.

Kevin Poulsen had many details, including an affidavit by FBI cyber-crime agent Albert Murray and an affidavit by Ari Baranoff, a US Secret Service Electronic Crimes Task Force agent working in the Eastern District of New York, in his June 28th WIRED Blog.


Baranoff deposed Olena Rakushchynets, the wife of the primary suspect, Yuriy Rakushchynets, who was arrested February 28, 2008 in their Brooklyn residence.

The search warrant against their residence had revealed that Yuriy participated in several Internet carding forums, and had purchased information used to encode blank ATM cards, which he then used to withdraw cash from ATMs. In February 2008 alone, he withdrew approximately $750,000, and on September 30, 2007 and October 1, 2007, he took out $100,000 in the 48 hour period. They also found $800,000 in cash ($690,000 in bags in their bedroom closet), a $34,000 Mercedes, and, from the pocketbook of Olena, 51 $20 bills in sequential order. Olena also had $99,000 in three separate safe deposit boxes, and had made more than $50,000 in deposits to the Ukranian National Federal Credit Union. (See WIRED's copy of the affadavit.

Yuriy, elsewhere called "Ryabinin", a 32-year-old Ukranian immigrant, Ivan Biltse, elsewhere called "Belyayev", 30, and Angelina Kitaeva, were all named in the indictment which covered activities from October 2007 to March 4, 2008. They were charged with "Conspiracy to Commit Access Device Fraud", and that they

unlawfully, willfully, and knowingly, and with intent to defraud, in an offense affecting interstate commerce, did effect and attempt to effect transactions, with one and more access devices issued to another person and persons, to receive payment and other things of value during a one-year period the aggregate value of which is equal to or greater than $1,000.


The indictment states Forfeiture claims on $2,000,000 in property, including the $800,000 seized from Yuriy on February 29, 2008 and an additional $800,000 seized from Ivan on March 4, 2008. (See WIRED's copy of the indictment.

Ivan Biltse, of Bensonhurst, New York, was originally arraigned on March 6, 2008 after being picked up for stealing $9,624 in 12 withdrawals from a Washington Mutal Bank ATM in Bay Ridge back on October 1. According to the New York Daily News, Ivan and Yuriy (who lived in Kensington) were cousins. (See Two Brooklyn Men ripped off $5M from ATMs around globe.)

The case actually started much earlier than that, when back on October 3, 2007, according to the FBI affadavit, First Bank notified the St. Louis Secret Service office that four "iWire" Prepaid Card accounts had been compromised. On just the dates September 30 and October 1, 2007, these four accounts were used to attempt more than 9,000 withdrawals from ATMs around the world, resulting in a loss of approximately $5 Million.

First Bank provided a list of withdrawal attempts, and several hundred of them came from banks in Brooklyn, including the Washington Mutual location that we already mentioned. Transaction and surveillance video pulled from several ATMs and nearby cameras showed:

a Caucasian male making withdrawals at the times and ATM terminals indicated in the First Bank Withdrawal Information for the Compromised Accounts. In the ATM video, this male is wearing a dark blue or black baseball cap emblazoned with the words "Top Gun" and a star and wings symbol, as well as a tan-colored sweatshirt or jacket with a dark blue or black front panel and dark blue or black trim at the zipper and collar.


Separately, on February 1, 2008, Citibank informed the FBI that a Citibank server(*) that processes ATM withdrawals at 7-11 convenience stores had been breached. A fraud alert system was established to flag all uses of these accounts, and the Citibank Withdrawal Information was used in a similar method. Surveillance video was pulled for many of these transactions, and some of them, including some on February 20, 2008 at the Citibank branch at 502 86th Street in Brooklyn, were made by the same individual, wearing the same "Top Gun" hat and sweatshirt as in the October withdrawals.

(Poulsen mentions that Citibank denies a breach. The USA Today article points out that the ATMs in question were not operated by Citibank, but by two other companies, Houston-based Cardtronics, and Brookfield, Wisconsin-based Fiserv. At this point, I don't think anyone has revealed what server was actually breached.)

This individual was quickly identified as Yuriy Ryabinin / Rakushchynets, and was found to have made $750,000 in fraudulent ATM withdrawals just in the month of February. How? Investigators searched Carding forums for individuals who were trading in First Bank or Citibank ATM information. One of these individuals was listing an ICQ number for contact. The ICQ had been registered earlier by "Yuri" a "29 years old male from brooklyn, USA".

A search for the same ICQ number showed that it belonged to a ham radio operator who signed his posts in Ham Radio websites with the same ICQ number. Some of those posts included photographs of Yuri in Dayton at a convention, wearing the same sweatshirt as the individual in the Washington Mutual and Citibank ATM surveillance videos.

A further search on the Ham Radio call sign that he used in these forums found that the FCC had sent him a letter, mentioning his call sign, regarding some minor administrative violations. The letter was addressed to "Mr. Yuriy Ryabinin, 679 Coney Island Avenue 2, Brooklyn, NY 11218".

A public records search found a Florida driver's license in that name, with a matching photograph. Ryabinin also had a Michigan driver's license under the name "Yuriy Rakushchynets".


Very Nice Work, Special Agent Albert Murray.

It will be interesting to see how much of the rest of the initial $5M in First Bank transactions can be identified.

You know I had to Google around a bit and find his call sign, right?

Yuriy Rakushchynets also had a hotmail account -- n2tta@hotmail.com, which he used to post a query looking for a job "within 2 hours drive of Brooklyn, NY". I have no idea what a "CQ-Contest" is, but Yuri was very active in them apparently, listed as a "fulltime operator" for events like the "CQWW SSB Soapbox", and other places giving his name and his call sign in things like:

Yuri, N2TTA, will be active as NP2/N2TTA between February 12-19th. His activity will include the ARRL DX CW Contest (February 16-17th) as NP2S and as a Single-Op/All-Band entry. Yuri informs OPDX that he will be active on CW and SSB on all bands including 30/17/12 meters.
(link.

Yeah, I guess with a couple mill of other people's money, you can buy some nice radios, eh, Yuri?

Tuesday, July 01, 2008

July Storm Worm gives us some Love

The authors of the Storm Worm must have had some good success with their "love theme" for last month's Storm Propagation Spam, because they have decided to repeat the theme today.

Right about midnight the UAB Spam Data Mine began to receive spam messages for the new Storm Worm.

After being directed to a website that looks like this:


we followed the links on the site to receive some fresh malware. How fresh was it? The executables, which were named "winner.exe" and "mylove.exe" depending on whether you follow the banner ad or the text link, were uploaded to VirusTotal where we found these results:


At our initial scan, of 33 different AV engines, only FOUR of them knew this was a virus, and only two could label it correctly. (Currently we are up to EIGHT AV products properly identifying this as storm. My university machine, which runs McAfee Anti-Virus, does not detect it with a fresh signature update.)

We have seen a wide variety of subject lines in the spam so far . . .

All I need is You
Always on my mind
Can't forget You
Can't stay away from you
Crazy in love
Crazy in love with you
Deep in my heart
Deeply in love with you
Fallen for you
For you...Sweetheart!
Hate that I love you
Here in my heart
Hold you close
I give my heart to you
I knew I Loved You
I'll never stope loving you
I'll Never Find Someone Like You
I'll Still Love You More
I Love Being In Love With You
I love you so much!
In your arms
Just you and me
Lost In Love
Lost In Your Eyes
Love me tender, love me true
Lovin' You
Lucky to have you
Madly in love
Miss you with all my heart
Missing you
My heart belongs to you
My heart to yours
My heart was stolen
Not the same without you
Only Wanna Be With You
Somebody loves you
Stand by my side
Together forever
We belong together
With all my love
With you by mi side
You are always on my mind
You are in my heart
You are my world
You are the ONE
You feel up my senses
You have touched my heart
You make my world beautiful
You make my world special

The domain names which have been used so far are:

bestlovelyric.com
gonelovelife.com
greatadore.com
knowholove.com
loveisknowlege.com
lovekingonline.com
lovemarkonline.com
loveoursite.com
makeloveforever.com
makingadore.com
makingloveworld.com
musiconelove.com
shelovehimtoo.com
superlovelyric.com
theplaylove.com
wantcherish.com
whoisknowlove.com
wholovedirect.com
wholoveguide.com

(Yes, we actually have spam samples for every one of these domains. For most we have MANY samples. That's what the Spam Data Mine does!)

All of these domains seem to be registered with Chinese Registrar "www.bizcn.com".

They use the nameservers (ns# as the prefix on each of these, ns, ns1, ns2, etc.):

likethisone1.com
lollypopycandy.com
verynicebank.com

and their own domain (ns1.wholoveguide.com, etc.)

The latter nameserver, verynicebank.com, was also used during the Beijing Earthquake version of the storm worm, described by f-secure. It served as the nameserver for "grupogaleria.cn", which was used in the attack described by F-Secure in their blog on June 19th. It also served as the nameserver for "nationwide2u.cn", although we are not yet sure of the purpose of that domain name.


We are actively seeking termination of the last few domains now (most are already down).

Monday, June 30, 2008

19 years old and headed to prison

Jason Michael Milmont, of Cheyenne, Wyoming, may be only 19 years old, but he's already a very successful cybercriminal. In this Los Angeles FBI Press Release, Milmont confessed to controlling between 5,000 and 15,000 remote victims' computers, which he infected through modified versions of Limewire, and through Instant Message spam messages which lead users to infected websites. Links he placed on MySpace and PhotoBucket were also used to spread his malware.

In January, sources such as ComputerWorld were calling Nugache a challenger to the Storm Worm for its virility, and implied that hackers "tied to the Russian Business Network" may be responible for an upgraded version. Nugache was one of the first botnets to be controlled via a Peer to Peer or distributed interface. Lacking a central Command & Control made it more difficult to identify the real controller of the network.

Milmont confessed to being the programmer -- so, it was a 19 year old in Wyoming, rather than a Russian boogie man in this case. Using a graphical user interface Milmont created, he could easily harvest the stolen credentials which the Nugache worm was gathering from his victims as they logged in to their banking and credit card sites. Infected machines could be remotely upgraded to receive new versions of the malware. The third version added the key-logging software to the malware kit.

Although Milmont harvested many credentials, he is only being asked to pay $73,866.36 in restitution, for purchases made using the stolen credit cards. Milmont shipped packages to vacant addresses where he then picked the packages up himself.

Jason studied computers at Laramie County Community College in Cheyenne. One of his instructors there, Roger Findley, described him as extremely intelligent but socially awkward.

By pleading guilty, Milmont will only be charged with a single count of a violation of 1030 (a)(4), accessing a computer without authorization with intention to defraud and obtain a thing of value. The maximum sentence to that plea would be 5 years and a $250,000 fine.

View the 22 page plea agreement here.


Links:

http://www.theregister.co.uk/2008/06/28/nugache_creator_plea_agreement/

Saturday, June 14, 2008

Chinese Hackers hit Congress?

The early news from US Representative Frank Wolf (R-VA) came out on June 11th, when Wolf submitted House Resolution 1263, calling for the Sergeant at Arms of the House of Representatives to "ensure that all Members, committees, and offices of the House are alerted to the dangers of electronic attacks on the computers and information systems used in carrying out their official duties and are fully briefed on how to protect themselves, their official records, and their communications from electronic security breaches". This is what the news story should have been -- that Representative Wolf calls for tighter security. A news-worthy and noble action, which is long overdue and would receive wide support from the Security Community.

The single line from his Resolution which has captured all of the attention came from this "Whereas" . . .


Whereas in subsequent meetings with HIR [The House Information Resources office] and officials from the Federal Bureau of Investigation, the outside source responsible for these incides was revealed to be located in the People's Republic of China;


More than 1100 news stories on Google mention the story, with some of the international mud-slinging using headlines like "US Accuses Chinese of Hacking Government Computers" which gained replies of "China says it's incapable of hacking Reps' computers".

Wolf didn't use such headlines -- the news story on his own website is headlined with Wolf Reveals House Computers Compromised by Outside Source. His office works with human rights activists and political dissidents around the world, and his emails and correspondence with some of these individuals was apparently compromised. He does say "My suspicion is that I was targeted by Chinese sources because of my long history of speaking out about China's abysmal human rights record." He also says that the Foreign Affairs Committee computers and that of other members who work "to help people who are suffering around the world" were similarly targeted.

That record is perhaps put most plainly in this impassioned speech by Representative Wolf from July 2007 -- Made in China, accuses China of poisoning toothpaste and toys, dumping products at below the cost of production on the international markets, arresting hundreds for religious beliefs and interring them in "slave labor camps", and compares their bid for the Olympics to that of the Nazis.

Wolf's words of warning on the Hill quote from several other sources as he issued his call for arms -- including a Congressional Research Service report indicating that 140 different foreign intelligence organizations regularly attempt to hack into the computer systems of US government agencies and US companies.

Joel Brenner, National Counterintelligence Executive of the Officer of the Director of National Intelligence used that figure in his speech here, and told CNN in October, it isn't just China, "there are about 140 foreign intelligence organizations trying to hack into the US government and US companies".

(Brenner also discussed the threat by the Chinese in this speech before the American Bar Association, where he says "From a purely fiscal point of view, it also means
the Chinese are leveraging the American R&D budget — your tax dollars and mine — in support of their own war-fighting capability.")

Wolf also made reference to the April 10, 2008 BusinessWeek story: The New E-Espionage Threat, which is a must read for anyone dealing with these threats both in corporate America and the government.

His reference to Shane Harris' alarming cover story of the National Journal magazine, China's Cyber Militia brings up other issues though. Is this fact? or fiction? I've had a copy of the "Northeast Blackout Report" on my hard drive for years, and am very familiar with the incident from both open and classified conversations. This is the first time that I've seen the blackout blamed on the People's Liberation Army, and frankly, I'm skeptical. Harris says:


One prominent expert told National Journal he believes that China’s People’s Liberation Army played a role in the power outages. Tim Bennett, the former president of the Cyber Security Industry Alliance, a leading trade group, said that U.S. intelligence officials have told him that the PLA in 2003 gained access to a network that controlled electric power systems serving the northeastern United States. The intelligence officials said that forensic analysis had confirmed the source, Bennett said. “They said that, with confidence, it had been traced back to the PLA.” These officials believe that the intrusion may have precipitated the largest blackout in North American history, which occurred in August of that year. A 9,300-square-mile area, touching Michigan, Ohio, New York, and parts of Canada, lost power; an estimated 50 million people were affected.


Rising to speak after Mr. Wolf, in support of his resolution, was US Representative Chris Smith (R-NJ), who used the opportunity to smear Google and Cisco, and call for support for his "Global Online Freedom" bill:


Google, for its part, has become the de facto center for China's ubiquitous anti-American, anti-Tibetan, anti-religious propaganda machine, while Cisco has made the dreaded Chinese secret police among the most effective in the world.


Like Wolf, Smith has reason to believe the attacks are sponsored by Beijing. He says:


The attackers hacked into files related to China. These contained legislative proposals directly related to Beijing, including the Global Online Freedom Act, e-mails with human rights groups regarding strategy, information on hearings on China--I chaired more than 25 hearings on human rights abuses in China--and the names of Chinese dissidents. While this absolutely doesn't prove that Beijing was behind the attack, it raises very serious concern that it was.


My conclusion is that it is clear that China is developing Cyber espionage capabilities, and it is clear that there are many attacks using Chinese IP addresses, but I have not yet seen any hard evidence that Wolf's computer was definitely attacked by "the Chinese". Even Mr. Smith's accusation indicates that the HIR staff told him "it came through or from a Chinese IP address".

That's why I refused to jump on the Evil China Bandwagon when I was interviewed by IDG News's Robert McMillan for the story he called: Weak Evidence Links Congressmen's Cyber Attacks to China. The truth is that there are many active criminal enterprises hosting "bullet proof servers" in China, which are used by a wide range of cyber criminals for all sorts of attacks. It would simplify things if we could return to a Reaganesque view of the world where all evil comes from a single location, but it takes more evidence than I have seen so far to jump on this particular bandwagon. Certainly there is a great deal of state-sponsored hacking from China, but until the details of each particular investigation are known, we can't make statements with the degree of certainty that Congressman Smith would like.

Friday, June 06, 2008

A Romantic June Storm

On June 2nd, starting at 5:53 PM, the UAB Spam Data Mine started receiving spam messages for the new version of the storm worm. The messages lead to a website titled "Who is loving you?" The "Love Riddles" web page invites you to "Just click here" to find out.


Its been four days since the new round of storm started up. How is the detection rate?

According to VirusTotal, only 6 of 32 AV engines are currently detecting this version of Storm:


What should you be looking for?

So far we've seen these email subjects:

I belong to you
I Wanna Be With You
Just you and me
Missing you
Missing you with every breath
My heart beats just for you
My heart was stolen
Nothing's Gonna Change My Love For You
Stand by my side
Together forever
We belong together
You are my world
You are the ONE
You make my world beautiful
You make my world special


Which contained a single phrase of text, followed by an IP address. Here are the Text lines in the body of the message:

Always on my mind
Can't stay away from you
Crazy in love with you
Dreaming 'bout you
Here in my heart
I want to be with you
I'll Still Love You More
In your arms
Just you and me
Lonely without you
Lost In Your Eyes
Lucky to have you
Missing you
Not the same without you
Somebody loves you
Stand by my side
Together forever
Wanna kiss you
We belong together
You are always on my mind
You are my world
You feel up my senses
You have touched my heart
You make my world special

And here are a list of some of the IP addresses we've seen advertised in the messages:

24.232.184.4
59.54.57.99
60.43.108.150
61.93.161.182
62.117.121.10
67.149.110.236 (*)
68.74.124.34
69.137.21.212 (*)
77.87.88.101
78.185.150.204
83.4.43.26
85.121.85.185
86.126.123.109
86.126.169.39
116.111.209.201
116.72.162.240
121.152.86.118
123.201.37.59
124.107.138.98
151.49.127.7
190.172.212.240
190.18.188.183
190.53.11.211
190.55.159.93
200.115.109.46
200.125.111.190
200.74.9.216
200.8.248.229
201.209.64.220
201.250.43.228
203.223.246.131 (*)
222.105.121.8

At this time, only 3 of these IPs, marked with an (*) actually delivered the malware.

Monday, May 19, 2008

38 Indicted in Los Angeles and Connecticut Phishing Cases

On April 23rd, Attorney General Michael B. Mukasey gave a speech in Washington DC where he revealed his new stance on International Organized Crime. He said in the speech that in the days of Robert Kennedy it was said mobsters would be "prosecuted for spitting on the sidewalk", and promised that he had 120 prosecutors and 500 FBI agents today who were going to be just as tough. He released a strategy document called Overview of the Law Enforcement Strategy to Combat International Organized Crime. In this document, he stresses that they are going to "Marshal Information and Intelligence" to "Prioritize and Target the Most Significant IOC Threats", and "Attack From All Angles". today's phishing indictments have turned out to be. To make it clear that this includes cybercrime, Threat #5 and the accompanying example from that document are given here:


THREAT 5: International organized criminals use cyberspace to target U.S. victims and infrastructure. International organized criminals use an endless variety of cyberspace schemes to steal hundreds of millions of dollars at a cost to consumers and the U.S. economy. These schemes also jeopardize the security of personal information, the stability of business and government infrastructures, and the security and solvency of financial investment markets.

One example of the intersection between organized crime and cybercrime is found in Romania. There, traditional Romanian organized crime figures, previously arrested for crimes such as extortion, drug trafficking and human smuggling, are collaborating with other criminals to bring segments of the young hacker community under their control. They organize these new recruits into cells based on their cyber-crime specialty and they routinely target U.S. businesses and citizens in a variety of fraud schemes.

One of the most lucrative schemes involves online auction fraud, where U.S. citizens are tricked into buying or selling goods, and never receive the funds or merchandise. One particular online criminal, using the online nickname “Vladuz” engaged in multiple fraud schemes, including hacking into the computers of eBay, the largest online auction retailer. On April 17, 2008, Vlad Duiculescu, a/k/a “Vladuz” was arrested in Romania by Romanian police officials and charged with crimes related to these schemes. It is believed that Vladuz is a participant in a ring of Romanian hackers who work together to develop joint U.S. targets for online frauds, share hacking techniques and launder proceeds from multiple crimes committed in the United States. U.S. prosecutors and law enforcement agents worked in Romania with Romanian officials to ensure that a case could be successfully prosecuted in Romania.


I've just reviewed the 77-page indictment unsealed today, and its clear the Attorney General is making good on his promise. To make sure the Romanians didn't miss it, Deputy Attorney General Mark Filip was in Bucharest Romania to do the press release alongside his Romanian counterparts. Here is a copy of the press release in Romanian.


At his Press Conference in Bucharest the DAG said:


The anonymity of the Internet makes it an ideal tool for this kind of fraud, and law enforcement agencies in the United States have conducted several recent investigations in partnership with our Romanian colleagues. We are proud to do so, and we are learning from each other as we jointly help to protect our citizens and people in other countries from this sort of theft and crime.

For the people arrested today, the indictments charge that the defendants sent out mass quantities of e-mails, known as "spam," to lure victims to go to fraudulent Websites that appeared to be legitimate banking or financial businesses. At those sites, victims were tricked into entering personal information such as financial and identity information and personal passwords—a scheme known as "phishing." That information was then harvested by “suppliers” who, in turn, sent the information to “cashiers” via real-time Internet chat sessions.

The cashiers used hardware encoders and related software to record the fraudulently obtained information onto the magnetic strips on the back of credit and debit cards. They then directed “runners” to withdraw money from automated teller machines. A portion of the withdrawals was wired by money transfer services, such as Western Union, back to the supplier. We believe these criminals defrauded literally thousands of individual victims out of several million dollars.

These arrests and charges are the result of a joint operation by the FBI and the Romanian General Inspectorate of Police, and the cases demonstrate the close cooperation our two countries have developed to fight international organized crime.


Some of the schemes were quite interesting. In a "Smishing" scam described in the indictment, an SMS Text Message would be received that says "We're confirming that you've signed up for our service. You will be charged $2 per day unless you cancel your order on this URL: www.trustme.com -- this would result in malware being planted on the visitor's browser.

Chat logs were included in the indictment, such as Panait sending a message to Tran, telling him "bro this are from my spam . . . super fresh . . . I will spam more . . . spammed like hell . . . used 7 remote desktops and 13 smtp servers, 5 root, and sent over 1.3 million emails."

Logs from August 2006 all the way up to January 2008 were included, that make it clear the roles of each of the defendants. Discussions and logs include counterfeit cards made for:

Allegheny Federal Credit Union, American National Bank of Texas, Arizona Federal Credit Union, Artesian City Federal Credit Union, Bank of America, BB&T (Banker's Bank & Trust), Boeing Employee's Credit Union, Bowdoinham Federal Credit Union, Capital One Bank, Citibank, Credit Union One, Downey Savings & Loan, epassporte, E-Trade, First Merit Bank, Flagstar Bank, Franklin Mint Federal Credit Union, Iowa League Corporate Central Credit Union, Jeffco Schools Credit Union, Langley Federal Credit Union, Mountain America Credit Union, NASA Federal Credit Union, North Island Credit Union, PointBank, Premier Credit Union, Premier Credit Union, Southern Lakes Credit Union, Southwest Federal Credit Union, Teacher's Credit Union, Telco Credit Union & Affiliates, Valley National Bank, Washington State Employees Credit Union, and the Waterbury Teachers' Federal Credit Union.

Caroline Tath and Tran were making their cash cards with laptop computers, Tath had a Dell Inspiron and an HP laptop, Gigatech flash drives, an MSR-206 encoder, an Operah card reader, and a software system called "CC2Bank 1.3", which was used to make the cards. Tran used a Sony Vaio laptop, and also provided software to defendant Lee, including a program called "TheJermMSR206". Lee used a Sony Vaio laptop and an MSR505C encoder.

Some of the defendants used their counterfeit cards to buy goods at WalMart and CostCo. Others purchased stock on E-Trade accounts, or used E-Trade accounts to purchase Postal Money Orders. Many cards were used to withdraw cash from ATM's in Los Angeles and Orange County. Some of those funds were transferred via Western Union or MoneyGram to Romania, where the data to make the cards had been received from on a "50/50" cashier's deal.

At least one defendant also shipped "refurbished notebook computers" to co-defendants in Romania.

Some of the ATM withdrawals were made using hotel room keys with the PINs written on the back in sharpie.

Romanians (indicted in Los Angeles):

Ovidiu-Ionut Nicola-Roman
Petru Bogdan Belbita
Stefan Sorin Ilinca, AKA AzZ, AKA Kahn, AKA Kahnpath
Sorin Alin Panait, AKA scumpic4u
Costel Bulugea, AKA The.Vortex
Nicolae Dragos Draghici, AKA Marius Bogdan, AKA Nonick
Florin Georgel Spiru, AKA niggaplease
Marian Daniel Ciulean, AKA spuickeru
Irinel Nicusor Stancu, AKA sicaalex
Didi Gabriel Constantin, AKA StauLaSoare, AKA Estaulasoare, AKA snoop
Mihai Draghici
Marius Sorin Tomescu, AKA Andrei
Lucian Zamfirache, AKA Krobelus
Laurentiu Cristian Busca, AKA italianu
Dan Ionescu, AKA m1nja
Marius (Last Name Unknown), AKA 13081981
Alex Gabriel Paralescu, AKA paraiul
Andreea Nicoleta Stancuta, AKA godfather

Romanians indicted in Connecticut:
(See FBI New Haven's Press Release )

residents of Craiova:
Ciprian Dumitru Tudor
Ovidiu-Ionut Nicola-Roman
Mihai Cristian Dumitru
Petru Bogdan Belbita, AKA "CA is SK", AKA Robert Wilson

residents of Galati
Radu Mihai Dobrica
Cornel Ionut Tonita
Cristian Navodaru

Perhaps more interesting would be the international partners who were also indicted, including:

Hiep Thanh Tran, AKA John Tran, AKA Sam Lam -- a US resident from Vietnam

Hassan Parvez, AKA XID - from Pakistan

US Citizens:
Sonny Duc Vo, Alex Chung Luong, and
Leonard Gonzales, AKA Bonecrusher

Vietnam Citizens:
Nga Ngo, AKA Christina Ngo
Thai Hoang Nguyen, Loi Tan Dang, Dung Phan - Vietnam

Cambodian Citizen:
Caroline Tath

Rolando Soriano, AKA Loco, AKA Danny Villalopez - from Mexico

Four other hackers remain at large, known only by their aliases:

Cryptmaster, PaulXSS, euro_pin_atm, and SeleQtor

We can look forward to the next big bust, because there seems no indication these fools are slowing down. When we visit some of the chat rooms where "kahnpath", for example, used to advertise his wares, we are immediately greeted with ads for people looking for "Cashout partners", and trying to sell an MSR-206 card writer for $400.

Saturday, May 17, 2008

Spanish Arrest D.O.M. Team

Spanish police announced the arrest today of five members of a prolific hacking team known as "D.O.M.". The D.O.M. team has been a political activism team active for quite some time. Zone-H, the "scoreboard of the underground", lists D.O.M as being #5 in prevalence of "Special" defacements - those against governments or major corporations or organizations. For all types of attacks, D.O.M is listed as #26, with 21,191 attacks credited to their account.

Update: Press Release from Spanish Police shows that the arrest operation was coordinated by "el Grupo de Seguridad Lógica de la Brigada de Investigación Tecnológica de la Policía Nacional" with cooperation from " agentes de la Brigada Provincial de Policía Judicial de Burgos, Málaga, Valencia y Sabadell". Congratulations to them all on their police work!

Recent defacements by the group list their members as:

an0de, ka0x, Xarnuz, and Piker

while hacks from earlier in the year listed:

crane0x, ka0x, Xarnuz, and S0cratex

We're not sure yet which were actually arrested, as the Spanish are protecting the identities of the group who are mostly minors, with two of those arrested being only 16 years old, and the other three being 19 and 20. Those arrested resided in four Spanish cities - Barcelona, Malaga, Valencia, and Burgos.

A Spanish speaking group, the actual membership has varied over time to include members from Spain, Argentina, and Mexico. For a short time a Brazilian hacker, "nwx0x" was also a member of their group, and "vpn0" and "Nitronet" have also been seen to claim membership. Their recent defacements have been Environmental Activism, decrying the pollution of rivers and the building of paper mills. The Spanish investigation began after a member of the group hacked the "Izquierda Unida" website and left supposedly "obscene messages" and caricatures of politicians on the site on March 3rd, a week prior to the March 9th election.

The actually words were:

"Tenemos algo en común, le dijo un presidente a un embustero..."
(roughly, "we have something in common, said the President to the liar/cheater" - which doesn't sound nearly as nasty as "obscene messages").

and the caricature may still be found on ImageShack, where it was originally hosted:


A spanish blogger at the time provided some clues as to what happened, including giving links to ka0x's profile on "spanish-hackers.com" (now offline) and pointing them to the current "D.O.M" website -- domlabs.org

Some of the more high-profile attacks credited to the group, at least from an American perspective, would include having hit the US government's National Cancer Institute with an SQL injection attack back in July of 2007, ( archived from Zone-H). In February, an0de defaced an MIT server with an anti-American, anti-Bush message, archive from Zone-H .

Members of the group are said to have hit NASA back in March, but it is unclear whether "Spanish Hackers Team"'s March defacement of "climate.gsfc.nasa.gov" is the same reference. Certainly its the same server that the closely allied hacker "SSH-2" hit as recently as April 25th, but we do have a positive reference of D.O.M member "an0de" hitting the NASA server "issues.worldwind.arc.nasa.gov" back in August 2007.

In a typical environmentally-motivated hack of Groton South Dakota's government website by the group in April 2007, the hacker used a gmail address: 3sk0rbut0@gmail.com and posted the message:


Defaced by ka0x

This is a cyber-protest against climatic change!!
Stop contamination!
(censored) to all governs that allow the contamination of the world!

we are: [ Arp; ka0x; an0nyph; xarnuz; Tequila ]

(SPain - Mexico - Argentina}


The spanish police say they are responsible for more than 21,000 website defacements including many government sites. (A statistic they surely got from Zone-H!) That matches what we see in the Zone-H archives, where hacks against the governments of India, Thailand, Turkey, Columbia, China, Malaysia, and others are readily found in the archives.

For several years the team ran a website, called "DomTeam.info", although their hosting was sketchy at best as they were run off numerous webservers. The original registration, from back in September of 2005, shows the email address "arcax.ath@gmail.com" as the contact address. "ATH" was another hacker group called "Arrow Team Hispanic", where Arcax partnered with KingMetal to cause script-kiddie type trouble to websites.

From the whois data from October of 2005, we find the meaning of the "D.O.M" name, as the whois information was changed to being registered to "Dark Owned Mafia". The members actually listed themselves in the WHOIS information later in 2005, when the whois "Street Address" was given as: "XgdnX - Davidu - Rootbox - ArCaX-ATH", the then current members of the group. That would remain the team's street address until November of 2007 when the domain was shut down by the Registrar (Melbourne IT).

ArCaX-ATH posted his "retirement from the underground" message on April 4, 2007, claiming at that time that he had been personally responsible for 10,880 website defacements. Here's that farewell message:


Bueno esto es algo que notaba desde hace algunos meses, mi poco tiempo para hacer las cosas del grupo D.O.M... y que muchos estaban anciosos de poder leer, así que hay les otorgo el siguiente regalo, baj la una reunión de costumbre. el domingo pasado he decidido delante de todos los miembros del grupo y con aprobación de los mimos, he decidido retirarme completamente de la scene Underground sin aviso por nuevo reintegro ni nada por el estilo, tenia pensado en hacerlo en octubre de este año cuando el team cumpliera los 2 años ... pero ya no podía tener en espera a los demás compañeros del grupo, aunque el echo de mi retirada no quiere decir que el grupo también se pare, se que anonyph los demás lo llevaran por el buen camino; agradezco en especial a her0 y ka0x que me llevaron a tomar la decisión correcta para el team. también se ha decido que la web de DOM no seguiría con portal ya que un portal requiere un cuidado exhaustivo con los foros y demás, se ha decido que me quedase con los 2 dominios (INFO y BIZ) para utilizarlo en mi blog personal, y otros proyectos personales... de ArCaX-ATH tendrán para rato eso sí, solo que con menos frecuencia que antes....


Although he was withdrawing, he states that "anonyph" will carry the team forward in the right direction.

ka0x was the one, however, who took the reins to set up the new website on January 31, 2008, and we find his gmail account listed in the registration for "domlabs.org" -- "ka0x01@gmail.com", with a (probably fake) Peruvian street address.

Using the same email, ka0x posted several exploits that he had written to the milw0rm collection of attack tools, including Remote SQL injection programs written in Perl, and a program to insert your own user information into an LDAP directory, which was bannered with this:


Title: LDAP injections
Author: ka0x
contact: ka0x01[!]gmail.com
D.O.M TEAM 2007
we: ka0x, an0de, xarnuz, s0cratex
from spain


Ten exploits and two papers are credited to ka0x on his milw0rm author page, including an 11 page paper on "Blind MySQL Injection" where he also lists the gmail address of one of his fellow team members, Piker, at piker0x90@gmail.com.

an0de also kept a blog at: http://buclenoapto.wordpress.com/

Thursday, May 15, 2008

Certificate Dangers?

The German Import House has a catalog where you can by a Dirndl dress or an Oktoberfest Party Hat.

https://germanimporthouse.sslpowered.com/germanimporthouse/nfoscomm/catalog/

The catalog gives its visitors the added sense of security by turning the address bar in my Firefox browser yellow, and adding a padlock to the address bar. When I float my mouse over the padlock, I get the "Authenticated by Equifax" popup.

When I click on it, it says:


SSL Server Certificate

Issued to
Common Name *.sslpowered.com
Serial Number: 08:90:D2

Issued By
Equifax Secure Certificate Authority

Issued On: 1/11/1008
Expires On: 2/10/2010


Unfortunately, someone put a Meadows Credit Union phish in a subdirectory of the catalog.


Visitors to that phishing site will see the same "warm fuzzy" yellow bar, and the same "Authenticated by Equifax" message.

Which brings me to the point of this article. We are all talking about Extended Validation Certificates, which will turn your address bar green, "proving" that the site is legitimate. What proof do we have that someone hasn't hacked the legitimate site and used it for an illegitimate purpose. That's what we see here with a "pre-" EV Certificate. German Import House is a legitimate site, and paid for an Equifax Certificate to prove so. However, the visitor to the Meadows Credit Union phishing site is ALSO going to see the Certificate behavior. But what does that prove?

How much danger are we in when we train our users that a colored address bar means they are safe - and then phishers hack those sites to host phishing content? The user sees a colored bar and a padlock -- one that really has a corresponding certificate on file -- and decides that its a safe site. Are EV Certs the answer? or just another way to train users that they don't have to think?


--

Wednesday, May 14, 2008

Indictments reveal $77 Million in Illegal Pill Sales

Congratulations to the Daytona Beach FBI, US Attorney Robert O'Neill, and their colleagues at IRS and FDA.

The Daytona Beach News reported the arrest of three Volusia county ringleaders with the headline Locals accused in $77 million Internet drug ring.

According to the indictment, Jive Network distributed approximately 4.8 million dosage units of Schedule III controlled substances and approximately 39.2 million dosage units of Schedule IV controlled substnaces to Internet customers who had no valid prescriptions. They serviced over 500,000 customer orders and generated more than $77 Million in revenues over a three year period.

Charged in the indictment were:

Jude LaCour, 35, Daytona Beach, Florida (Jive Network Owner)
Jeffrey LaCour, 60, South Daytona, Florida (Jive Network Director of Operations)

whose charges included money laundering and drug trafficking offenses involving the sale of controlled substances over the Internet. (The elder LaCour was profiled May 11th in this story: Rx Suspect has Mixed Local History

Hudsen Smith, 36, Deland, Florida (Jive Network Director of Pharmacy/Physician Operations)

and the following physicians, who were paid to do the "medical reviews" for patients who had no prescriptions.

Christopher Tobin, 41, Wilmington, North Carolina (Physician)
Akhil Baranwal*, 34, Pennsylvania (Physician)
Alexis Roman Torres, 54, Puerto Rico (Physician)
Andrew DeSonia, 47, Indiana (Physician)
Marget Fulmore (McIntosh), 52, Charlotte, North Carolina (Physician)
Abel Lau, 36, Tulsa, Oklahoma (Physician)
James Pickens, 72, Midvale, Utah (Physician)

The prescriptions were filled by several pharmacists, but the only one charged in this indictment is:

Geunnet Chebssi, 56, Spencerville, Maryland (Pharmacist)

Customers, who had no prescriptions, accessed the websites and purchased the controlled substances after completing a short health history questionnaire. Identities were not verified and medical records were not submitted.

The announcement of this indictment has been a long time coming. Online drug stores have known that The Jive Network, also known as "Celestial Group Inc", has been in trouble since at least April of 2005. A note from one such online drugstore dated April 24, 2005, read:


The Jive Network, also trading as Celestial Group Inc, were closed on the morning of April 19, 2005 as part of an investigation by DEA and FBI. To date no charges have been laid and the owner of the online pharmacy group, Jude LaCour is not in custody and has not been charged with any offences. (...) The pharmacy sites that are affected are: ePharmacist, Pillvalue, Pillstore, InstantPills, and Cyberpills.


An update on May 12, 2005 added this:


We believe Jive Network are trying to get back online and are clearing ePharmacist, PillStore, PillValue, and CyberPill orders that were held up around April 19th. Over the past 2 weeks, they seem to be either refunding customers or sending product.


At that time, Jive sent a letter to their affiliates explaining the situation. (Quoted from the "rx-affiliate" forum at "ABestWeb.com", posted April 29, 2005):


Dear Affiliate,

You may have heard the news that our offices were served with a search warrant last Tuesday, April 19th, 2005.

However, NO ARRESTS were made. No Charges were filed.

This is an obvious attempt by the DEA and FBI to try and lump us in with a group of 20 other companies/individuals that had been under
investigation, and who WERE arrested around the same time.

We want to share with you that we are NOT related to nor connected with these 20 in any way.

Jive Network has ALWAYS done everything by the book and beyond.

We have broken no laws.

We know that some of your checks have bounced. This is because the search warrant also allowed them to seize all bank accounts. When we say all,
we do mean ALL! We realize that apologizing for the difficulty this has caused you does very little, but we want to assure you of this: As soon as we are able to correct it, we will.

As to the current status, late last week, we put the websites back online. We have our internet connections and the equipment we need to start
processing orders again. However, until our accounts and other matters are operational, we are not taking orders at this time.

Additionally, something is going on with our phone lines. This is likely part of this defamatory attempt on us, so we are working to uncover and
resolve that problem as well.

When we are fully operational, we will immediately begin processing orders.

Lastly, to those of you that have emailed us telling us that you are with us, we want to express how sincerely all of us appreciate that support.
We have read comments such as, "You guys are the best ever in the industry, just let me know when I can switch my links back".

This kind of response is more than encouraging to us, and the truth is that we want to be here for as much as you are here for us. We do understand
what you are experiencing.

Please understand that the delay in sending you some kind of direct communication has been due to the circumstances of this situation, NOT
BECAUSE WE DIDN'T WANT TO TALK TO YOU.

You can be sure that this situation will not stop us. We might "look" much different in the future, we will still be us, the same "Jive Network
Team" working hard for you.

While we are uncertain as to when we will come back online, you can be certain that when we do, our entire business will be stronger and even better
than before. A team that has been through an event like this and stands firm, is a team that can accomplish anything.

Stand firm with us. We will accomplish great things, together.

Sincerely,

Jive Network


(The same letter can also be found here)

In February 2006 the note was updated again that "XL Pharmacy" had acquired the chain of online drugstores, and was standing by to fill your needs. "XLPharmacy prescriptions drugs are made by world renowned International pharmaceutical companies such as Novartis, Cipla Abbot, Aventis, Bayer, Cipla, Dr. Reddy's, Merck, Eli Lily, GlaxoSmithKline, and Ranbaxy. All prescription drugs are shipped in the manufacturers' original package and have the manufacturers' original seal for your safety.

The link provided is still live:http://www.xlpharmacy.com/index.php?img=4&kbid=1325. The helpful FAQ on that site, which claims to have been online since 2004, says:


In all cases orders require a prescription prior to shipment. If you do not have a prior prescription you will be asked to complete a online medical consultation and it will them be reviewed by a licensed physician who may or may not issue a medical prescription based upon your medical consultation. If your online medical consultation was not approved by the physician you will then need to provide a medical prescription from your local physician by fax to us prior to the shipment of your order.


And yes, this replacement pharmacy is still recruiting . . .according to their website:


Experience the highest payout commission and the best Affiliate Support by telephone, live chat and email. XLPharmacy.com pays the highest direct commission and the highest second tier commissions in the industry. Payments are made by bank transfer or epassporte weekly. Please contact the program manager to arrange for your preferred payment options and commissions structure. Commissions are paid up to 45%.


I can't swear that to be accurate. There were several competing affiliate programs who apparently were believed to have purchased Jive Networks customer list. LaCour and Jive Network were also the feature of an issue of The Ripoff Report claiming they had gone back into business operating "rxwebdrugstore.com, realprescriptions.com, rxwebmeds.com" and others. The owner of "Secure Medical" posted a rebuttal to this though claiming they were not related, and that their database had been compromised.

In a letter written by Haden Smith back on Aug 20, 2004, he claims there are more than 100 online prescription websites using their fulfillment services, and that their pharmacies earn between $3,000 and $10,000 per day profit.

The chat boards used by the online pharmacies and their customers are lighting up with news stories about the arrests:

Rx Affiliate Forum posters want to know "are affiliates next"? In reply, the poster was reminded "What about the 8 affpower affiliates" who were arrested? Several posters say that advertising is not illegal as long as the affiliates don't take the payments or touch or ship the drugs they are "just like Google or Yahoo" - only advertisers.

epharmacywatch.com, which provides this list of online pharmacies and their associated "Consultation Fees" and user ratings. Their conversation forum for talking about US-based online pharmacies has over 100,000 posts! The site has 117,791 registered users as of this morning. It will be interesting to see if their reaction to the news goes beyond mere reporting of the indictments.

* - curious coincidence in names here . . . this name, and city, came from court documents, but there is an Akhil Baranwai in Georgia accused of the same sort of behavior (i vs L at the end of the last name)

Monday, May 12, 2008

TJX and Dave & Busters

If you've visited a Dave & Busters, you know these are a great place for grown-ups to go out and play. I've been to several events at the Atlanta location, and enjoy the Virtual Reality games there. I never thought I would see a Dave & Busters story come up on the news-ticker that I have watching for new TJX stories, but that is what happened this morning.

You will probably recall the story of Maksym Yastremskiy (Maksik), a Ukrainian citizen arrested in Turkey for his role in trading enormous volumes of credit cards which could all be traced back to the TJX debacle. He was back in the news today with two other hackers, Aleksandr Suvorov (JonnyHell) from Estonia, and Albert Gonzales (Segvec). The charges are that the first two ran a scam involving the installation of packet sniffers into thte cash register systems at 11 Dave & Buster's restaurants. Just the Islandia, New York location was credited with 5,000 customer's credit card data leading to more than $600,000 in fraudulent purchases. Segvec is charged only with "wire fraud conspiracy", in that he purchased some of this data from Maksik.

The indictment was posted on the ABC News website.

The 27 counts against the first two are:

Count One: Conspiracy to Commit Wire Fraud
(knowingly and intentionally conspiring to devise a scheme and artifice to defraud D&B, its customers, and the financial institutions that issued the customers' credit and debit cards, and to obtain money and property...by means of materially false and fraudulent pretenses, representations and promises, and attempting to do so by means of wire communication in interstate and foreign commerce . . . )

Counts 2-5: Wire Fraud
(installing a packet sniffer, and reactivating it at D&B Store #2 in Islandia, New York, on 5/18/07, 6/9/07, 7/23/07, 8/14/07.)


Count 6: Conspiracy to Possess Unauthorized Access Devices

Count 7-9: Possession of Unauthorized Access Devices
(the "access device" in question being log files containing "15 or more credit and debit card account numbers".)
(Title 18, Section 1029(a)(3))
(Title 18, Section 1029(c)(1)(A)(i))


Count 10-12: Aggravated Identity Theft
(Title 18 Section 1028A(a)(1), (b), (c)(5))

Count 13: Conspiracy to Commit Computer Fraud
(Title 18 Section 371 and 3551)

Count 14-16: Unauthorized Computer Access Involving an Interstate Communication
(Title 18 Section 1030(a)(2)(C))
(Title 18 Section 1030(c)(2)(B)(i))

Count 17-19: Unauthorized Computer Access to Obtain Things of Value
(Title 18 Section 1030(a)(4))
(Title 18 Section 1030(c)(3)(A))

Count 20-23: Unlawful Transmission of Computer Codes
(Title 18 Section 1030(a)(5)(A)(i))
(Title 18 Section 1030(a)(5)(B)(i))
(Title 18 Section 1030(c)(4)(A))

Count 24-27: Interception of Electronic Communications
(Title 18 Section 2511(1)(a))
(Title 18 Section 2511(4)(a))

Oh yeah, and they are going to go for Criminal Forfeiture of all losses.

All the way back in June 2007, Maksik and Segvec are on the way towards losing their e-gold accounts, according to this testimony from US Secret Service agent Roy Dotson, who names e-gold account number 1751848 as belonging to Maksik, and 3584940 as belonging to Segvec.

From that affadavit:


“Segvec”: “Segvec” is a vendor of stolen financial information on the carding
website Makafaka and accepts payment for his contraband in e-gold. A search and review of the e-gold database revealed number 2464856 – which has as its contact name “segvec.” According to information related to me from agents of New Scotland Yard’s National Terrorist Financial Investigation Unit regarding email communications they had with Douglas Jackson in April 2007, Douglas Jackson was aware that “segvec” was a Ukrainian carder.

An analysis of “segvec”’s account number 2464856 yielded the following results:
The account was created in October 2005. There were 93 transfers into the account with a value of 1524.80951 grams ($845,545.60).

20 of the 90 transactions, which total 726.623113 grams ($410,750.00) and occur between February and May 2006, are transfer of funds from account 1751848, “Maksik’s Job”


“Maksik”: “Maksik” is a known vendor of stolen credit card information, stolen
financial accounts, and fraudulent Ukranian passports on the Shadowcrew, Mazafaka, and Carderplanet carding websites and accepts payment for this contraband in e-gold. A search and review of the e-gold database revealed account number 1751848, with the account name “Maksik’s Job,” and contact email addresses of info@maksikjob.com and maksik@maksik.biz. Several memo fields in the transaction record for e-gold account number 1751848 indicate carding activity, including, for example, “1-27 order amex” (i.e., an order for a stolen American Express credit card number), “Happy H4xOr Dumps” (i.e., stolen credit card information), “For 20 classics” (i.e., a type of credit card). A search and review of the e-gold database also revealed e-gold account number 3399565, with the account name “Maksik’s account,” and containing a contact email address of Maksik@maksik.cc. A review of this account also shows many transactions with other e-gold accounts controlled by known carders, including e-gold account number 2567183 (controlled by “Lord kaisersose” – a known vendor of stolen credit card information), and e-gold account number 2874688 (controlled by “u26" – a provider of credit card pre-authorization services to vendors)


Yastremskiy was arrested in Turkey in July 2007, where he remains in jail.

Suvorov was arrested in Germany in March 2008.

Gonzalez was arrested in Miami in May 2008 by the US Secret Service.

Friday, May 09, 2008

Digital Certificates Update

A quick update from the previous post.

The Digital Certificates spam campaign against Merrill Lynch continues, but the good guys seem to be recovering their lead. Of the 9 domain names used in the spam campaign last night:

876536784k.com
2376540m.com
1291logon.org
10000993m.com
374286434d.com
8447652a.com
1291logon.biz
1291logon.net
1291logon.com

only one was live when my morning report was run this morning.

2376540m.com

did load the web page shown in the previous blog entry, and attempted to download the file:

MLBusinessCentreCERTv6704.exe

but this time the download was detected by McAfee anti-virus and blocked as "Spy-Agent.bg"

Much better. We'll see if we can make 2376540m.com go away shortly.

Tuesday, May 06, 2008

Digital Certificate Alert!

UAB Computer Forensics is investigating yet another "Digital Certificate" phishing attack -- this time with Merrill Lynch as the target.

The traditional definition of phishing requires the website that the customer visits to request personal information, such as the userid and password to an online account, or credit card or bank account information. In this case, no personally identifiable information is requested. Instead, the emails and the destination website tell the potential victim that Digital Certificates will make their online financial experiences safer. This rings true with consumers, who are certain to have heard about the advantages of certificates, especially as the "Extended Validation Certificates" (the ones that turn your browser address bar green if you are on a real site?) are increasingly proclaimed by companies like DigiCert,
Verisign,
and Thawte to be the Next Big Thing in security.

It is this increased consumer awareness that is leading to the current rounds of victimization. In this scheme, the consumer receives an email, informing him that his financial accounts will be more secure if they upgrade to digital certificates, or that their current digital certificate has expired and needs to be upgraded. If they follow the link, they are taken to a website where they receive more information about the importance of the upgrade, and are given instructions to "install" their digital certificate, with a link to download the installation program.

The installation program is of course a virus. The first Digital Certificate malware we investigated, against Bank of America, ended in early April, but the new round, which includes Comerica Bank, Colonial Bank, and now Merrill Lynch, is still going strong, with Comerica being a nearly daily target with more than 250 domain names used in the fraud. Colonial Bank has only been targeted on two days, with 22 domain names used, and now Merrill Lynch, which launched yesterday with the domain names

1291logon.info and 1291logon.com

(I confirmed that both websites were taken offline before publishing this article.)

The Merrill Lynch version of the Malware is called "Papras.dk" by most of the anti-virus programs that detect it. The first version of the Colonial Bank trojan was called "Papras.dh", and the first version of the Comerica Bank trojan that we looked at was called "Papras.dc". More evidence that these are originating from a common source.

As with most emerging threats, common anti-virus products are not immediately blocking the threat. For instance, F-Prot, McAfee, and Symantec, do not show on VirusTotal as having detection for this threat. McAfee engineers have previously complained to me that VirusTotal is not an accurate way of knowing whether they have detection. I run McAfee on my own work desktop though, (for balance, I run Symantec at home), and when I do an AV update (to DAT version 5289.0000, dated May 6 2008), and then scan the file, it does not detect.

The sad part about the failure of common AV engines to detect this virus is that this file is a BINARY IDENTICAL MATCH for the Colonial Bank version of the trojan that we analyzed and reported on April 30. One week later, and the two largest AV companies still have no detection.


The current email looks like this:


MERRILL LYNCH BUSINESS CENTER IS CHANGING

Merrill Lynch develops new solutions that deliver instant,
comprehensive online banking and protection against evolving
computer security threats.

Dear Merrill Lynch Business Center Customer:

In an effort to better serve you, the following changes to the
daily processing procedures will go into effect on Tuesday, May 6th:
We’ll be launching new ml.com Business Centre homepage

In addition to a fresh look, the new Merrill Lynch website will provide:
-VIP CLUB
-Easier access to login
-Easier ways to contact and locate us
-Access to more information on what we offer and what we do Online
Please discover new Business Centre homepage now:
Continue>>

Copyright 2008 Merrill Lynch & Co., Inc.


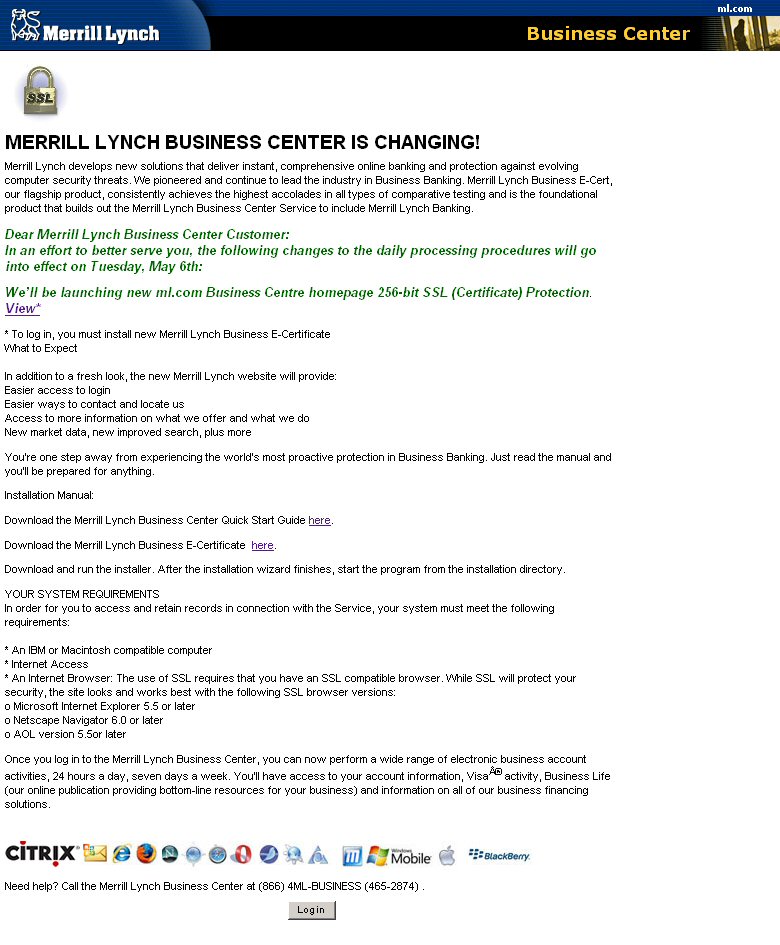
And the website that it pointed us to looked like this:


Now, put on your Sherlocke Holmes hat and try this one yourselves. Can you detect any similarities with this email?


Comerica TM Connect Web Bank Renewal

Certificate Renewal
Personal (Smartcard) e-Cert & Personal e-Cert
Certificate owner must renew the certificate before expiry date.
Your certificate expiration date - 1may 2008.
The system will send email (Certificate Renewal Notice) to the certificate owner ten
days and 3 hours before the certificate is due to expire, if it has not been renewed.
Upon receiving the renewal notice, certificate owner is required to connect to
Comerica Bank Certificate Management System and present the client certificate.
Secure Server e-Cert & Developer e-Cert
Certificate owner has the responsibility to renew the certificate before expiry date.
Successful renewed application will receive an email notification from Comerica Bank.
Applicant can just browse to the URL stated in the email and then download the certificate.

Download now>>

2008 Comerica Treasury Management Connect Web (SM) Version 4.2


How about this email?


Connection-Colonial Bank Renewal

Certificate Renewal
Personal (Smartcard) e-Cert & Personal e-Cert
Certificate owner must renew the certificate before expiry date.
Your certificate expiration date - 1may 2008.
The system will send email (Certificate Renewal Notice) to the certificate owner ten
days and 3 hours before the certificate is due to expire, if it has not been renewed.
Upon receiving the renewal notice, certificate owner is required to connect to
Colonial Bank Certificate Management System and present the client certificate.
Secure Server e-Cert & Developer e-Cert
Certificate owner has the responsibility to renew the certificate before expiry date.
Successful renewed application will receive an email notification from Colonial Bank.
Applicant can just browse to the URL stated in the email and then download the certificate.

Download now>>

2003 Colonial Bank, N.A.


Thursday, April 17, 2008

Dear CEO . . . You are Commanded to Go Phishing!

This week has been busy with yet another Spear Phishing campaign being launched against the Execs of US-based companies. This is not a new trend by any means. In my presentation at the DOD CyberCrime Conference this year, "Spear Phishing: Hackers Target High Value Targets", I shared information about the October "Better Business Bureau" spear phishing attack and the January "US Department of Justice" spear phishing attack. Its clear that this round is a continuation of these.

In the current round, the email contains the real name of the executive (we have confirmed it is not only CEOs, so that is also consistent with the previous attacks), and their real telephone number in the body of the email. Here are some excerpts from one such email . . .


SUBPOENA IN A CIVIL CASE

Case Number:

(numbers here)
United States District Court

YOU ARE HEREBY COMMANDED to appear and testify before the Grand Jury of
the United States District Court at the place, date, and time specified
below.

...

Please download the entire document on this matter (follow this link)
and print it for your records.

...

Failure to appear at the time and place indicated may result in a
contempt of court citation. Bring this subpoena with you to the
courtroom and present it to the bailiff.


The initial domain used in the attack, "cacd-uscourts.com" was registered through the Registrar "Web4Africa" on April 12th. On Monday, we had the good fortune that someone reported this phish to the CastleCops PIRT Team, where it was assigned PIRT #792683. Monday evening, PIRT received an email back from Web4Africa informing us that the site had been disabled, which they did by changing their NameServers to "suspended1.web4africa.net" and "suspended2.web4africa.net", as you can see in their Current WHOIS record.

I wasn't able to fetch the malware the first round, as I was away from my lab at the incredible Usenix LEET 08 Workshop, where I was able to meet some security heroes of mine, Thorsten Holz and Neils Provos, the authors of Virtual Honeypots: From Botnet Tracking to Intrusion Detection. (Subliminal mode on -- Buy this Book! -- Subliminal Mode Off).

I got home Wednesday afternoon and went straight to the lab, only to learn that the Phisher was stupid enough to immediately try again. When I arrived in the lab, I checked for other sites hosted by the original nameservers and saw that a new domain name had been registered early Tuesday morning. They chose a different name, "casd-uscourts.com", which they hosted on the exact same IP as the other box, (which incidentally hosts several other malware sites which infect their visitors by installing software via "IFRAME" and Encrypted Javascript techniques).

We used CastleCops to get the site shut down again last night, but not until we first made some screen shots and infected a goat machine with the malware to see what it would do. (Thanks to two of my UAB CIS graduate students for staying late and working on this last night!)

The site is using ActiveX to deliver its malware, and requires an Internet Explorer browser, as you can see from the two screen shots below:


Several people have said "No CEO would click on a subpoena in email!" That's probably true. The CEO would probably send it to the corporate counsel, who would click on the subpoena in email.

Regardless WHO clicks on it, here is what happens if someone does:

The browser goes to "Acrobat.php", which causes the creation of a hidden file called \Windows\system32\Acrobat.dll.

The registry is modified by placing the value: "rundll3d acrobat.dll Anit" in the registry key: \HKLM\Software\Microsoft\Windows\CurrentVersion\Run

A listening port is opened (in our case it was on port 1900).

Every 60 seconds, the machine notifies this computer in China of its infected status by visiting a URL like this:

http://124.94.101.48/MMM/parse.php?mod=cmd&user=MachineName

where MachineName is the system name of the machine in question.

That is probably all the details I'll share for now.

If anyone has observed network traffic going to this IP, there is a very good chance someone in your network is infected. I'd love to know what other communications your infected machine is exhibiting. Please do send me an email!

Wednesday, April 09, 2008

"Grey Pigeon" banking trojan leads to jail time in China


On April 3, computing.co.uk reported the arrest of four Chinese men for breaking into the online bank accounts of their fellow citizens. The report was high on theory and low on details. For the moment we will ignore the "spin" being placed in this story elsewhere in the media -- does this mean the Chinese government wants to stop hackers, but only if they are hacking other Chinese? -- let's just examine the facts.

The four men, who have the surnames of Duan, Wei, Li, and Ruan, according to an April 1 report from Shanghai Daily News received sentences ranging from 8 years to 2.5 years. They were also fined 155,000 yuan, or about $20,000 USD. The sentencing occurred in the Luwan District People's Court.

According the Shanghai Daily News report, the hackers did their work by using a hacker tool called "Grey pigeon 2006vip". After planting this software on various websites, visitors to those websites became infected with a trojan which stole their userids and passwords when they logged on to their bank. We call this type of infection a "Drive By Infector". All that is necessary to be infected is to visit a website hosting the malware.

Li's role was to hack the website and install "Grey Pigeon". Duan received the accounts and transferred the money out of the victim accounts to an account controlled by the hackers. Wei and Ruan had the hands-on job of withdrawing the cash from ATM machines.

The withdraws mentioned in the trial occurred on April 11, 2007 and May 12, 2007.

Luwan district, which is part of Shanghai, has seen similar cases of this type recently, including the the conviction of Bai Yongchun last September, who was also convicted of stealing money by using the Grey Pigeon software.

Grey Pigeon can be found being discussed at "hacker120.com", which also goes by the name of "www.hkop.cn", in a forum called: 黑客攻防技术专区

The current version of Grey Pigeon (Grey Pigeon 2008, or 微尘灰鸽子2008免杀版), has been available at hacker120.com since January 31, 2008. The virus tries to edit your registry to make itself a Windows Service, by adding the tag:

HKLM\SYSTEM\CurrentControlSet\Services\Windows XP Vista

to your registry, with a pointer to itself. The originally downloaded file is named "hacker.com.cn.ini", but this file is renamed to an ".exe" with the same name as it is copied to create the Windows Service named "Windows XP Vista".

Sophos detects the current version of Grey Pigeon as "Troj/Mdrop-BQA", and has protected against it since Feb 2008, according to this Sophos information page.

In China, the Grey Pigeon family is prevalent enough that Chinese anti-virus company "Rising" has a special detection program for it, which can be downloaded from their website (GPDetect.exe), where they have a link to Grey Pigeon information from their main website homepage. (The information page about Grey Pigeon has been being updated since originally published by Rising in 2005!)

Thursday, April 03, 2008

Welcome Cornelius Tate, our new NCSD!


Today Brian Krebs broke the story in his Washington Post "Security Fix" blog, that Cornelius Tate had been named to head the Department of Homeland Security's National Cyber Security Division.

Cornelius Tate is a perfect example of a Computer Science major making a difference in the world of Cyber Crime. Tate received his bachelor of science in Computer Science from the University of Mississippi in 1985, but when a friend of his joined the Secret Service during Tate's junior year, he realized that he would rather be investigating computer crimes than writing code. (Source: DiversityCareers.com)


Like former NCSD Director, Jerry Dixon, Tate worked at the IRS after graduating from college. US-CERT will not be something new to him -- in 2002, Tate served as the Carnegie Mellon University's Software Engineering Institute as the "resident liaiason" from the USSS to the CERT Coordination Center (CERT/CC). Tate initiated the use of CERT/CC staff in high profile protection planning as part of the "Critical Systems Protection Initiative" (CSPI) which included having CERT members travel with the Secret Service to prepare cyber systems for events such as the 2002 Olympic Games and Super Bowl XXXVI.

Tate also recognizes the value of R&D. In this feature from SEI's CERT/CC Tate says of the Service, "We bring hands-on experience, and the CERT/CC provides a research and development capability that extends beyond the scope of our traditional protective mission."

While at CERT/CC, Tate was part of the "Insider Threat Study" research staff that lead to the development of the "MERIT" system, which we actually had presented in Birmingham at the joint "FBI InfraGard/USSS Computer Crimes Working Group" meeting in 2006. MERIT stands for "Management and Education of the Risk of Insider Threats", and we learned a great deal from the presentation.

When Tate was assigned to the Presidential Protective Detail, he served as the Supervisory Administrator for Technology Systems, and was actively involved in tracing email and Internet-based threats to the White House and its residents.

InfraGard members will know of Mr. Tate's work, not only from his participation in the famous InfraGard Houston conferences, but also in the form of their DHS-appointed Protective Security Advisors. Mr. Tate oversaw all of our nation's PSA's in his position as the Director of Field Operations for the Protective Security Division. In Birmingham we are very grateful for the active participation of our PSA in the Birmingham Chapter of InfraGard.

Congratulations on the new position, Mr. Tate. As an InfraGard President, and a Cyber Crime Researcher, I wish you well, and look forward to working with you and your staff in your new endeavors.

In Nigeria, Yahoo Boys picked up by EFCC Raids

Cyber Cafes in Akure in the state of Ondo, and Onitsha, in the state of Anambra were raided today. The locals have a term for the type of cyber criminal who lurks in these cafes. They call them "yahoo boys".


(image from "Hey CyberCafe" in Onitsha, not included in the raid, just a sample picture of an Onitsha-based cybercafe)

In Akure, agents of the EFCC (Econonmic and Financial Crimes Commission), acting as customers, mingled about the crowd, bought airtime, and began using computers themselves while observing the activities of those around them. Once their suspicions were confirmed, they rose and identified themselves, requiring each of the users of the cafe to remain on site until they had confirmed what email addresses they had been using, and what activities those email addresses had been performing. "This Day" in Lagos reports that at least one Yahoo Man jumped out the window when the raid began. This Day reports that the following day the cyber cafes were nearly empty, "leaving only those with serious business".

In Onitsha, things went a bit differently, according to The Nigerian Tribune, with officers arriving in an unmarked Toyota van and blocking off the road leading to Main Market to prevent the flight of cyber cafe operators.

Sixteen arrests were made, primarily of Yahoo Boys, who spend their days reading and sending scam emails hoping to encourage rich Americans to part with their money. At least one cyber cafe operator was also arrested, and several computers were confiscated as evidence.

The most fascinating part of this story, however, is not in the current day's news. For the story behind the story we have to go back to March 17th, when the President of Nigeria, Umaru Yar'Adua, announced that he was planning to establish a separate body known as the National Cyber Crimes Commission. The bill, which was described in Nigeria's Business Day Online, was called necessary precisely because the EFCC cannot effectively "handle the cyber crimes in addition to its other responsibilities". Business Day Online's source said the activities of the Yahoo Boys are having a negative impact on the government and on investment and a separate agency was required to handle the situation.

The bill to establish the National Cyber Crimes Commission is still in the National Assembly. With the president leaning on both chambers for quick passage, is the EFCC trying to prove the bill is unnecessary?

Public opinion has turned against the EFCC, as represented in a recent column in the IndependentNGOnline, called "Heroes, Yahoo Boys, and the Rest of Us". (Sorry, the article is no longer online, the author "angrymichael2004@yahoo.com" has a regular column called "Conversations of an Angry Man"). The column calls the Yahoo Boys "Criminal Eaglets", and warns the EFCC that if they continue to "deliberately overlook" the Yahoo Boys, they are going to use their relative wealth to graduate to the true houses of power.

The columnist continues "I had the impression that the EFCC may rather wait for these fraudsters to cut their teeth in politics or public administration before going after them", but he then goes on to say those who chase down and catch these crooks are the true heroes. While the President is welcoming as national heroes Nigerian boxer, Samuel Peter, and the Under 17 World Championship Nigerian soccer team, the Golden Eaglets, the columnist recommends the President proclaim those who catch cyber criminals National Heroes instead.

Whether the NCCC is formed, or whether the EFCC decides to take their cyber crime responsibilities more seriously, the benefit on the American public should be positive. For today, the EFCC are Crime Fighting Heroes. I hope it continues!

Tuesday, April 01, 2008

AKILL Convicted - Are we safer now?

Last night the BBC World Service called to ask me what I thought of the AKILL conviction. We primarily discussed that the news here should not be that AKILL is the criminal mastermind of the Internet, but that its Good News that we've managed to catch someone and get a conviction.


AKILL, Owen Thor Walker, AKA "Snow Whyte" (Whyte was his mother's maiden name), AKA "Snow Walker" (note to hackers, don't use your own name as your alias), is a troubled young man living in New Zealand. Up until his conviction he was a quiet, gifted programmer, who worked for Trio Software Development. The media is painting him to be the ring leader of a worldwide criminal enterprise which controls 1.3 Million computers and has caused $20 Million USD in damages.

There is no question Walker was brilliant. He is diagnosed with Asperger's Syndrome, a disorder in the same family as autism, characterized by very poor social interaction, and a fixation on a narrow range of intellectually challenging pursuits that often involve a high degree of repetition. His mother says he left school at age 14, largely because of problems with bullies, and completed his education via correspondence courses.

But what were the actual charges? ComputerWorld New Zealand is reporting this morning that the only damages they have charged him with are $13,000 in costs which the University of Pennsylvania incurred in recovering from a Botnet attack he launched against the TAUNET service housed at UPenn. (See ComputerWorld.nz

The Sydney Morning Herald, which ran a picture of Walker and his mother in this article of Feb 29, 2008, said:

Walker was arrested in November last year in the northern city of Hamilton as part of an international investigation into a cyber crime network accused of infiltrating 1.3 million computers and skimming millions of dollars from victims' bank accounts.


But the original story which brought AKILL into the International eye was the charges brought by the FBI under Operation Bot Roast II, which Forbes magazine mentioned like this as recently as yesterday:

The FBI's deputy assistant director of its Cyber Division, Shawn Henry, points to the November arrest of the hacker known as AKILL, an 18-year-old in New Zealand running a botnet of 50,000 computers.


The other charge that we know about AKILL is that he has been accused "by Dutch authorities" of being part of a scheme where hackers installed advertising software on computers they compromised. One of the other targets of Operation Bot Roast II was Robert Matthew Bentley, of Panama City, Florida. Bentley was convicted of his charges on March 6, 2008, according to this FBI Jacksonville Press Release.

I am saying that it is very likely that this is actually the same scheme that AKILL was tied up in, (but haven't found the proof of that yet). Bentley was accused of installing software for a scheme called "Dollar Revenue". Dollar Revenue was fined $1.54 Million USD by Dutch authorities in a scheme where hackers were paid 15/100 of a Euro for installing the adware on European computers, or 25 cents for installing the adware on American computers. (See this PC World article)

These types of revenues fall more in line with what was said during AKILL's trial, where the judge was considering whether to force Walker to pay restitution of "$8,000". New Zealand media are reporting that Walker plead guilty to infecting "at least 20,000" computers, and his bank accounts show that he had received payments of "$40,000 NZD". (See for example this New Zealand TV station's report.

What actually was the "criminal mastermind" activity that AKILL performed? He took source code for a previous botnet program and made some slight modifications to it. Detective Inspector Peter Devoy of the New Zealand police confirmed in interviews that AKILL is responsible for the "AkBot" malware. (See Security IT World's story for more.) (Devoy was also the one quoted in the original New Zealand Police press release: Waikato Police investigate cyber-crime

How was Walker caught? It looks like a good job of International Cooperation, but one lynchpin in the investigation goes back to making poor choices in friends online. Ryan Goldstein, AKA Digerati, has been a troublemaker for years. Ryan, a 21-year old student at UPenn, was a member of a hacking group called "TeamLoosh", and couldn't decide what color his hat should be.

TeamLoosh leader, rofles, basically went on a character-assassination rampage against Ryan, posting defaming photographs and emails intended to show that Ryan was a pedophile anywhere that he saw Ryan making posts. Some of these appeared in places like "governmentsecurity.org", posting links to a file named: http://www.teamloosh.com/txt/Digerati-Exposed.zip (now offline).

Ryan was angry, but having been banned from several places because of these accusations, he behaved in his typical fashion. He promised AKILL access to several "elite" hacker websites where he still had influence, if he would help him get revenge. The DDOS, intended to punish the TAUNET Internet Relay Chat servers which had banned "Digerati", was said to include 50,000 attacking computers, which were launched against TAUNET by AKILL.

The Digerati Indictment is available from the Pennsylvania US Attorney's Office. It reveals the exact nature of the payment offered to AKILL. (Quoting from page 5 of the indictment:


"I can get you some good private stuff, i can also pay you, to take taunet down...i have access to a lot of stuff you might want...www.findnot.com/servers.html - i have a legit login/pass for that, guaranteed to work through 2007 at least...undetected, unreleased bifrost (trojan) beta with 100% av (antivirus) and fw (firewall) bypass."


I'm very pleased that Ryan/Digerati and Owen/AKILL/Snow Whyte have been apprehended, but the point of what I tried to say on BBC World Service this morning was let's not make this a fishing story. We haven't landed Moby Dick here. We haven't stopped a "Criminal Mastermind". We caught a few juveniles with anger management and social problems, who made $40,000 selling hacked computers to a Dutch advertising company and attacked a University chat room because the boys there told another boy he was not their friend any more.

Its a message that International Law Enforcement Cooperation is working, at least between the Dutch, the FBI, and the New Zealanders, but we still have a long way to go before the Internet is going to be a safe place to play.

-----

Corrections Made:
Ryan Lee, ryan1918, has pointed out an error in the original version of this posting. Ryan Lee (ryan1918) is *NOT* Digerati, and should not be confused with Ryan Goldstein.

To Priest, stm, rofles, Gammarays, Zerofool2005 - thanks for the comments - send me an email. Happy to learn more and have a more accurate article.