Friday, July 11, 2014

New GameOver Zeus Variant uses FastFlux C&C

Over on the Malcovery Security Blog yesterday we covered a new version of GameOver Zeus (see: GameOver Zeus Mutates, Launches Attack ) that was distributed in three spam campaigns on July 10, 2014. At the bottom of that blog post, we're sharing a detailed "T3 Report" by analysts Brendan Griffin and Wayne Snow that gives all the details. In our reporting yesterday we mentioned that the new bot is using a Fast Flux Command & Control structure and that it is using a Domain Generation Algorithm to allow the malware distributed in the spam to locate and connect to the Command & Control servers.

I wanted to geek that a bit deeper for those who want more details on both of those subjects. First, let's look at the Fast Flux.

Fast Flux Command & Controlled Botnet

Fast Flux is a technique that allows a criminal who controls many servers to obfuscate the true location of his server by building a tiered infrastructure.

Sometimes there are additional "tiers" or levels of misdirection. We don't yet know how many layers there are in this newGOZ botnet.


(click to enlarge)

Here's the flow . . .

  1. the newGOZ criminal pays the Cutwail spammers to send out emails to infect new victims
  2. the Cutwail spammer sends out his emails. On July 10th, they were "Essentra Past Due" and emails imitating M&T Bank and NatWest Bank
  3. while many people delete the emails, ignore the emails, or have them blocked by spam, SOME people click on the emails
  4. the ".scr" email attachment infects their computer and starts generating "Domain Generation Algorithm" domains.
  5. each domain is queried for. the Bot computers say "Hey, Internet! Does this domain exist?"
  6. on July 10th, cfs50p1je5ljdfs3p7n17odtuw.biz existed ... "the Internet" said "Yes, this exists and NS1.ZAEHROMFUY.IN is the Nameserver that can tell you where it is."
  7. When most nameservers tell the address of a computer, they give a "Time To Live" that says "The answer I'm giving you is probably good for 24 hours" or 2 days, or a week, or whatever. But the Nameserver used in a FastFlux Bot, like, NS1.ZAEHROMFUY.IN, usually gives a "Time To Live" answer that says "The answer I'm giving you is only good for about 5 minutes. After 5 minutes, you need to ask me again in case the address has changed."
  8. NS1.ZAEHROMFUY.IN receives constant updates from "newGOZ Criminal" of servers all over the world (but mostly in Ukraine) that have been hacked. Almost every time you ask the nameserver "Where is the newGOZ domain?" it will give you a different answer.
  9. the "FastFlux C&C" boxes are now running nginx proxy software that says "Whatever you ask me, I will ask the servers at the Evil Lair of newGOZ. Whatever the Evil Lair of newGOZ wants to say, I will pass back to you.
  10. Updates from the Evil Lair get passed back THROUGH the FastFlux Proxy and give the newGOZ bots new malware or commands
  11. All traffic to and from the newGOZ bot, whether it is the bot "checking in" or the criminal pushing an "update" goes through one of the proxies, which are constantly changing.

Fast Flux newGOZ resolutions

All of the servers (or workstations) in this table were used as Fast Flux C&C nodes last night by the newGOZ botnet. We'll keep tracking this with friends from ShadowServer, DissectCyber.com and others and sharing this information with our trusted partners, but I wanted to throw out this example. If you have ability to look at "Net Flow" for any of these computers, you may be able to help us locate "The Evil Lair of the newGOZ Criminal." (Which sounds like a lot more fun than just looking at packet dumps, doesn't it? Sorry, this isn't my job, it is my passion. Geeks have to convince themselves they are Fighting Evil or we would get bored. Since the first GOZ enabled the theft of $100 Million or so ( for more see as an example Crooks Seek Revival of GameOver Zeus Botnet where Brian even shares the FBI Wanted Poster of the guy who is thought to be behind Zeus.

2014-07-10 20:37:10-05 92.248.160.157 92.248.128.0/17 OLYMPUS-NSP-AS ZAO _AKADO-Ekaterinburg_,RU 30868 RU ripencc
2014-07-10 20:38:04-05 108.20.219.49 108.20.0.0/16 UUNET - MCI Communications Services, Inc. d/b/a Verizon Business,US 701 US arin
2014-07-10 20:38:36-05 113.163.13.252 113.163.0.0/19 VNPT-AS-VN VNPT Corp,VN 45899 VN apnic
2014-07-10 20:39:03-05 114.46.251.46 114.46.0.0/16 HINET Data Communication Business Group,TW 3462 TW apnic
2014-07-10 20:39:24-05 176.108.15.141 176.108.0.0/19 KADRTV-AS Cadr-TV LLE TVRC,CZ 57800 UA ripencc
2014-07-10 20:40:39-05 178.150.136.252 178.150.136.0/22 BANKINFORM-AS TOV _Bank-Inform_,UA 13188 UA ripencc
2014-07-10 20:40:52-05 37.25.4.162 37.25.0.0/19 BELCOMUA-AS ZAO _Belcom_,UA 25385 UA ripencc
2014-07-10 20:41:05-05 69.143.45.75 69.143.0.0/16 CMCS - Comcast Cable Communications, Inc.,US 33657 US arin
2014-07-10 20:41:18-05 77.242.172.30 77.242.172.0/24 UHT-AS UHT - Ukrainian High Technologies Ltd.,UA 30955 UA ripencc
2014-07-10 20:41:31-05 85.29.179.7 85.29.179.0/24 ORBITA-PLUS-AS ORBITA-PLUS Autonomous System,KZ 21299 KZ ripencc
2014-07-10 20:47:43-05 24.101.46.15 24.101.32.0/19 ACS-INTERNET - Armstrong Cable Services,US 27364 US arin
2014-07-10 20:47:56-05 37.115.246.222 37.115.0.0/16 KSNET-AS _Kyivstar_ PJSC,UA 15895 UA ripencc
2014-07-10 20:48:10-05 67.68.99.137 67.68.96.0/22 BACOM - Bell Canada,CA 577 CA arin
2014-07-10 20:48:23-05 70.24.225.245 70.24.224.0/22 BACOM - Bell Canada,CA 577 CA arin
2014-07-10 20:48:43-05 75.76.166.8 75.76.128.0/17 WOW-INTERNET - WideOpenWest Finance LLC,US 12083 US arin
2014-07-10 20:48:57-05 76.127.161.112 76.127.128.0/17 COMCAST-7015 - Comcast Cable Communications Holdings, Inc,US 7015 US arin
2014-07-10 20:49:21-05 91.197.171.38 91.197.168.0/22 INTRAFFIC-AS Intraffic LLC,UA 43658 UA ripencc
2014-07-10 20:49:44-05 99.248.110.218 99.224.0.0/11 ROGERS-CABLE - Rogers Cable Communications Inc.,CA 812 CA arin
2014-07-10 20:50:02-05 100.44.184.18 100.44.160.0/19 WAYPORT - Wayport, Inc.,US 14654 US arin
2014-07-10 20:52:54-05 109.207.127.59 109.207.112.0/20 TELELAN-AS Teleradiocompany TeleLan LLC,UA 196740 UA ripencc
2014-07-10 21:07:24-05 178.214.223.104 178.214.192.0/19 UOS Ukraine Optical Systems LLC,UA 42546 UA ripencc
2014-07-10 21:07:56-05 212.22.192.224 212.22.192.0/24 FREENET-AS Freenet Ltd.,UA 31148 UA ripencc
2014-07-10 21:08:11-05 31.133.118.121 31.133.118.0/24 ENTERRA-AS Private Enterprise _Enterra_,UA 48964 UA ripencc
2014-07-10 21:08:24-05 37.229.149.56 37.229.0.0/16 KSNET-AS _Kyivstar_ PJSC,UA 15895 UA ripencc
2014-07-10 21:08:45-05 46.119.77.105 46.119.0.0/16 KSNET-AS _Kyivstar_ PJSC,UA 15895 UA ripencc
2014-07-10 21:09:21-05 98.14.34.141 98.14.0.0/16 SCRR-12271 - Time Warner Cable Internet LLC,US 12271 US arin
2014-07-10 21:09:37-05 98.109.164.97 98.109.0.0/16 UUNET - MCI Communications Services, Inc. d/b/a Verizon Business,US 701 US arin
2014-07-10 21:12:28-05 109.162.0.21 109.162.0.0/18 KSNET-AS _Kyivstar_ PJSC,UA 15895 UA ripencc
2014-07-10 21:12:41-05 178.140.183.193 178.140.0.0/16 NCNET-AS OJSC Rostelecom,RU 42610 RU ripencc
2014-07-10 21:13:42-05 178.158.135.20 178.158.134.0/23 ISP-EASTNET-AS EAST.NET Ltd.,UA 50780 UA ripencc
2014-07-10 21:28:15-05 192.162.118.118 192.162.116.0/22 ANOXIN FIZICHNA OSOBA-PIDPRIEMEC ANOHIN IGOR VALENTINOVICH,UA 39056 UA ripencc
2014-07-10 21:28:18-05 208.120.58.109 208.120.0.0/18 SCRR-12271 - Time Warner Cable Internet LLC,US 12271 US arin
2014-07-10 21:28:18-05 213.111.221.67 213.111.192.0/18 MAINSTREAM-AS PP MainStream,UA 44924 UA ripencc
2014-07-10 21:28:18-05 24.207.209.129 24.207.128.0/17 CHARTER-NET-HKY-NC - Charter Communications,US 20115 US arin
2014-07-10 21:28:18-05 46.181.215.20 46.180.0.0/15 ELIGHT-AS E-Light-Telecom,RU 39927 RU ripencc
2014-07-10 21:28:19-05 68.45.64.5 68.44.0.0/15 CMCS - Comcast Cable Communications, Inc.,US 33659 US arin
2014-07-10 21:28:19-05 75.131.252.100 75.131.224.0/19 CHARTER-NET-HKY-NC - Charter Communications,US 20115 US arin
2014-07-10 21:28:19-05 91.196.60.108 91.196.60.0/22 ARHAT-AS PE Bondar TN,UA 50204 UA ripencc
2014-07-10 21:28:19-05 91.243.218.157 91.243.192.0/19 ID-TELECOM-AS Intellect Dnepr Telecom LLC,UA 59567 UA ripencc
2014-07-10 21:28:19-05 96.246.91.160 96.246.0.0/17 UUNET - MCI Communications Services, Inc. d/b/a Verizon Business,US 701 US arin
2014-07-10 21:28:19-05 134.249.11.2 134.249.0.0/16 KSNET-AS _Kyivstar_ PJSC,UA 15895 UA ripencc
2014-07-10 21:49:21-05 188.190.5.162 188.190.0.0/19 ASINTTEL Inttel Ltd.,UA 56370 UA ripencc
2014-07-10 21:49:22-05 5.248.110.252 5.248.0.0/16 KSNET-AS _Kyivstar_ PJSC,UA 15895 UA ripencc
2014-07-10 21:49:22-05 31.43.162.96 31.43.160.0/19 KRASNET-UA-AS Krasnet ltd.,UA 50576 UA ripencc
2014-07-10 21:49:22-05 31.135.144.54 31.135.144.0/22 Technical Centre Radio Systems Ltd.,UA 20539 UA ripencc
2014-07-10 21:49:22-05 37.112.195.140 37.112.192.0/22 KRSK-AS CJSC _ER-Telecom Holding_,RU 50544 RU ripencc
2014-07-10 21:49:22-05 46.119.181.97 46.118.0.0/15 KSNET-AS _Kyivstar_ PJSC,UA 15895 UA ripencc
2014-07-10 21:49:22-05 50.83.36.2 50.83.32.0/21 MEDIACOM-ENTERPRISE-BUSINESS - Mediacom Communications Corp,US 30036 US arin
2014-07-10 21:49:23-05 176.8.92.131 176.8.0.0/16 KSNET-AS _Kyivstar_ PJSC,UA 15895 UA ripencc
2014-07-10 21:49:23-05 176.98.12.218 176.98.0.0/19 CRYSTAL-AS Crystal Telecom Ltd,CZ 49889 UA ripencc
2014-07-10 21:49:23-05 178.137.8.215 178.137.0.0/17 KSNET-AS _Kyivstar_ PJSC,UA 15895 UA ripencc
2014-07-10 22:08:06-05 95.110.45.151 95.110.0.0/17 JSCBIS-AS OJSC _Bashinformsvyaz_,RU 28812 RU ripencc
2014-07-10 22:08:08-05 176.8.21.85 176.8.0.0/16 KSNET-AS _Kyivstar_ PJSC,UA 15895 UA ripencc
2014-07-10 22:08:08-05 178.150.89.211 178.150.89.0/24 BANKINFORM-AS TOV _Bank-Inform_,UA 13188 UA ripencc
2014-07-10 22:08:08-05 188.231.191.140 188.231.191.0/24 FREENET-AS Freenet Ltd.,UA 31148 UA ripencc
2014-07-10 22:08:08-05 80.66.79.74 80.66.76.0/22 RISS-AS LLC _Ris-Tel_,RU 20803 RU ripencc
2014-07-10 22:08:09-05 81.200.148.6 81.200.144.0/20 ARTEM-CATV-AS JSC Artemovskoye Interaktivnoe Televidenie,RU 41070 RU ripencc
2014-07-10 22:08:09-05 95.46.219.178 95.46.219.0/24 VITEBSK-TV-ISP-AS OAO Vitebskiy Oblastnoy Techno-Torgoviy Center Garant,BY 50528 CZ ripencc
2014-07-10 22:08:09-05 95.78.166.17 95.78.128.0/18 ERTH-CHEL-AS CJSC _ER-Telecom Holding_,RU 41661 RU ripencc
2014-07-10 22:29:38-05 178.214.169.234 178.214.160.0/19 LUGANET-AS ARTA Ltd,UA 39728 UA ripencc
2014-07-10 22:29:38-05 188.16.223.225 188.16.192.0/18 USI OJSC Rostelecom,RU 6828 RU ripencc
2014-07-10 22:29:38-05 194.246.105.173 194.246.104.0/23 ASN-FUJILINE Trade House _Inet_ Ltd,UA 31000 UA ripencc
2014-07-10 22:29:39-05 70.75.230.0 70.75.0.0/16 SHAW - Shaw Communications Inc.,CA 6327 CA arin
2014-07-10 22:29:39-05 78.137.17.91 78.137.0.0/19 MCLAUT-AS LLC _McLaut-Invest_,UA 25133 UA ripencc
2014-07-10 22:29:39-05 176.117.86.162 176.117.80.0/20 LURENET-AS PP _Lurenet_,UA 50643 UA ripencc
2014-07-10 22:48:09-05 213.111.163.205 213.111.128.0/18 ALNET-AS PP SKS-Lugan,UA 35804 UA ripencc
2014-07-10 22:48:10-05 99.249.29.20 99.249.0.0/16 ROGERS-CABLE - Rogers Cable Communications Inc.,CA 812 CA arin
2014-07-10 22:48:10-05 109.254.35.236 109.254.0.0/16 DEC-AS Donbass Electronic Communications Ltd.,UA 20590 UA ripencc
2014-07-10 22:48:10-05 136.169.151.67 136.169.128.0/19 UBN-AS OJSC _Ufanet_,RU 24955 RU ripencc
2014-07-10 22:48:10-05 176.102.209.127 176.102.192.0/19 KUTS-AS Center for Information Technologies _Fobos_ Ltd.,UA 39822 UA ripencc
2014-07-10 22:48:10-05 178.141.160.202 178.141.0.0/16 MTS-KRV-AS MTS OJSC,RU 44677 RU ripencc
2014-07-10 22:48:10-05 178.213.191.181 178.213.184.0/21 SKYNET-UA-AS FOP Shoruk Andriy Olexanderovich,UA 196777 UA ripencc
2014-07-10 22:48:10-05 184.152.102.159 184.152.0.0/16 SCRR-12271 - Time Warner Cable Internet LLC,US 12271 US arin
2014-07-10 22:48:10-05 213.110.137.77 213.110.128.0/19 SUNNET-AS PE Gritcun Oleksandr Viktorovich,UA 47889 UA ripencc
2014-07-10 23:08:56-05 91.219.254.25 91.219.254.0/24 MONOLITH-AS LLC MONOLITH.NET,UA 48230 UA ripencc
2014-07-10 23:08:58-05 109.87.83.213 109.87.80.0/22 BANKINFORM-AS TOV _Bank-Inform_,UA 13188 UA ripencc
2014-07-10 23:09:00-05 178.137.176.9 178.137.128.0/17 KSNET-AS _Kyivstar_ PJSC,UA 15895 UA ripencc
2014-07-10 23:09:00-05 78.109.46.210 78.109.46.0/24 SIBRON-AS Closed Joint Stock Company COMSTAR-Regiony,RU 13155 RU ripencc
2014-07-10 23:09:00-05 80.70.71.41 80.70.64.0/20 ENERGYTEL Energytel LLC,UA 51317 UA ripencc
2014-07-10 23:27:45-05 71.75.52.101 71.75.0.0/16 SCRR-11426 - Time Warner Cable Internet LLC,US 11426 US arin
2014-07-10 23:27:45-05 176.8.72.36 176.8.0.0/16 KSNET-AS _Kyivstar_ PJSC,UA 15895 UA ripencc
2014-07-10 23:27:45-05 178.74.214.94 178.74.192.0/18 EVEREST-AS _Everest_ Broadcasting Company Ltd,UA 49223 UA ripencc
2014-07-10 23:27:45-05 178.141.9.72 178.141.0.0/16 MTS-KRV-AS MTS OJSC,RU 44677 RU ripencc
2014-07-10 23:27:45-05 188.230.87.17 188.230.80.0/21 ABUA-AS LLC AB Ukraine,UA 43266 UA ripencc
2014-07-10 23:27:45-05 37.229.79.59 37.229.0.0/16 KSNET-AS _Kyivstar_ PJSC,UA 15895 UA ripencc
2014-07-10 23:27:45-05 62.16.38.131 62.16.32.0/19 FPIC-AS CJSC _COMSTAR-regions_,RU 15640 RU ripencc
2014-07-10 23:49:05-05 176.113.227.109 176.113.224.0/19 LUGANET-AS ARTA Ltd,UA 39728 UA ripencc
2014-07-10 23:49:05-05 193.106.184.92 193.106.184.0/22 BOSPOR-AS Bospor-Telecom LLC,UA 42238 UA ripencc
2014-07-10 23:49:05-05 46.172.231.154 46.172.224.0/19 TOPHOST-AS SPD Kurilov Sergiy Oleksandrovich,UA 45043 UA ripencc
2014-07-10 23:49:05-05 74.129.235.88 74.128.0.0/12 SCRR-10796 - Time Warner Cable Internet LLC,US 10796 US arin
2014-07-10 23:49:05-05 77.121.129.181 77.121.128.0/21 VOLIA-AS Kyivski Telekomunikatsiyni Merezhi LLC,UA 25229 UA ripencc
2014-07-10 23:49:05-05 78.27.159.112 78.27.128.0/18 DOMASHKA-AS Domashnya Merezha LLC,UA 15683 UA ripencc
2014-07-10 23:49:05-05 91.196.55.7 91.196.52.0/22 KOMITEX-AS PP KOM i TEX,UA 30886 UA ripencc
2014-07-10 23:49:06-05 94.153.23.170 94.153.0.0/16 KSNET-AS _Kyivstar_ PJSC,UA 15895 UA ripencc
2014-07-10 23:49:06-05 109.87.222.148 109.87.222.0/24 BANKINFORM-AS TOV _Bank-Inform_,UA 13188 UA ripencc
2014-07-11 00:07:17-05 178.215.178.112 178.215.176.0/20 FENIXVT-AS Private Enterprise Firma Fenix VT,RU 39399 UA ripencc
2014-07-11 00:07:19-05 195.90.130.19 195.90.128.0/18 ROSNET-AS OJSC Rostelecom,RU 6863 RU ripencc
2014-07-11 00:07:19-05 37.25.118.55 37.25.96.0/19 WILDPARK-AS ISP WildPark, Ukraine, Nikolaev,UA 31272 UA ripencc
2014-07-11 00:07:19-05 37.229.215.18 37.229.0.0/16 KSNET-AS _Kyivstar_ PJSC,UA 15895 UA ripencc
2014-07-11 00:07:19-05 87.244.34.238 87.244.32.0/21 SUNLINK-AS Sunlink Telecom ISP, Tula, Russia,RU 35401 RU ripencc
2014-07-11 00:07:19-05 91.219.233.40 91.219.232.0/22 REALWEB-AS Private Enterprise RealWeb,UA 41161 UA ripencc
2014-07-11 00:07:20-05 173.95.149.72 173.92.0.0/14 SCRR-11426 - Time Warner Cable Internet LLC,US 11426 US arin
2014-07-11 00:07:20-05 178.150.221.2 178.150.220.0/23 BANKINFORM-AS TOV _Bank-Inform_,UA 13188 UA ripencc
2014-07-11 00:07:20-05 178.151.165.182 178.151.165.0/24 BANKINFORM-AS TOV _Bank-Inform_,UA 13188 UA ripencc
2014-07-11 00:28:03-05 109.87.42.122 109.87.40.0/21 BANKINFORM-AS TOV _Bank-Inform_,UA 13188 UA ripencc
2014-07-11 00:28:04-05 109.200.228.156 109.200.224.0/19 BREEZE-NETWORK TOV TRK _Briz_,UA 34661 UA ripencc
2014-07-11 00:28:04-05 31.135.226.91 31.135.224.0/20 TRYTECH-AS Trytech Ltd.,RU 44056 RU ripencc
2014-07-11 00:28:04-05 46.172.145.109 46.172.128.0/19 UTEAM-AS Uteam LTD,UA 49125 UA ripencc
2014-07-11 00:49:18-05 109.229.198.37 109.229.192.0/19 PRONET_LV SIA _PRONETS_,LV 43075 LV ripencc
2014-07-11 00:49:20-05 178.165.98.17 178.165.64.0/18 CITYNET-AS Maxnet Autonomous System,UA 34700 UA ripencc
2014-07-11 00:49:20-05 195.114.145.69 195.114.144.0/20 DATAGROUP PRIVATE JOINT STOCK COMPANY _DATAGROUP_,UA 21219 UA ripencc
2014-07-11 00:49:20-05 5.58.15.61 5.58.0.0/18 NOLAN-AS Lanet Network Ltd,UA 43120 UA ripencc
2014-07-11 00:49:20-05 46.147.186.225 46.147.184.0/22 NEOLINK CJSC _ER-Telecom Holding_,RU 34590 RU ripencc
2014-07-11 00:49:20-05 46.219.50.56 46.219.50.0/24 FREENET-AS Freenet Ltd.,UA 31148 UA ripencc
2014-07-11 00:49:20-05 89.185.24.218 89.185.24.0/21 TVCOM-AS TVCOM Ltd.,UA 34092 UA ripencc
2014-07-11 00:49:20-05 94.158.73.89 94.158.64.0/20 BIGNET-AS PE Yuri Stanislavovich Demenin,UA 43668 UA ripencc
2014-07-11 00:49:20-05 95.47.151.247 95.47.148.0/22 TKS-AS Sumski Telecom Systems Ltd,UA 41967 CZ ripencc
2014-07-11 01:09:51-05 71.227.196.156 71.227.128.0/17 COMCAST-33650 - Comcast Cable Communications, Inc.,US 33650 US arin
2014-07-11 01:09:52-05 87.224.164.135 87.224.128.0/17 TELENET-AS OJSC Rostelecom,RU 35154 RU ripencc
2014-07-11 01:09:52-05 93.127.60.17 93.127.60.0/23 ALKAR-AS PRIVATE JOINT-STOCK COMPANY _FARLEP-INVEST_,RU 6703 UA ripencc
2014-07-11 01:09:52-05 109.227.127.25 109.227.96.0/19 MCLAUT-AS LLC _McLaut-Invest_,UA 25133 UA ripencc
2014-07-11 01:09:52-05 178.151.9.221 178.151.9.0/24 BANKINFORM-AS TOV _Bank-Inform_,UA 13188 UA ripencc
2014-07-11 01:09:52-05 178.151.154.233 178.151.154.0/24 BANKINFORM-AS TOV _Bank-Inform_,UA 13188 UA ripencc
2014-07-11 01:09:52-05 194.187.108.182 194.187.108.0/22 TERABIT TERABIT LLC,UA 29491 UA ripencc
2014-07-11 01:09:52-05 37.229.149.148 37.229.0.0/16 KSNET-AS _Kyivstar_ PJSC,UA 15895 UA ripencc
2014-07-11 01:09:52-05 46.118.151.246 46.118.0.0/16 KSNET-AS _Kyivstar_ PJSC,UA 15895 UA ripencc
2014-07-11 01:09:52-05 46.219.77.143 46.219.77.0/24 FREENET-AS Freenet Ltd.,UA 31148 UA ripencc
2014-07-11 01:28:30-05 178.137.232.234 178.137.128.0/17 KSNET-AS _Kyivstar_ PJSC,UA 15895 UA ripencc
2014-07-11 01:28:31-05 178.150.177.83 178.150.176.0/23 BANKINFORM-AS TOV _Bank-Inform_,UA 13188 UA ripencc
2014-07-11 01:28:31-05 178.151.14.223 178.151.14.0/24 BANKINFORM-AS TOV _Bank-Inform_,UA 13188 UA ripencc
2014-07-11 01:28:31-05 178.151.227.102 178.151.227.0/24 BANKINFORM-AS TOV _Bank-Inform_,UA 13188 UA ripencc
2014-07-11 01:28:31-05 188.231.170.228 188.231.170.0/24 FREENET-AS Freenet Ltd.,UA 31148 UA ripencc
2014-07-11 01:28:31-05 5.34.112.211 5.34.0.0/17 SATELCOM-AS SA-Telcom LLP,KZ 35566 KZ ripencc
2014-07-11 01:28:31-05 46.56.64.196 46.56.64.0/19 MTSBY-AS Mobile TeleSystems JLLC,BY 25106 BY ripencc
2014-07-11 01:28:31-05 46.173.171.188 46.173.168.0/22 BEREZHANY-AS Galitski Telekommunications Ltd,UA 49183 UA ripencc
2014-07-11 01:28:31-05 176.215.86.177 176.215.84.0/22 KRSK-AS CJSC _ER-Telecom Holding_,RU 50544 RU ripencc
2014-07-11 01:49:53-05 31.202.226.233 31.202.224.0/22 FORMAT-TV-AS MSP Format Ltd.,UA 6712 UA ripencc
2014-07-11 01:49:53-05 46.33.59.6 46.33.56.0/22 BLACKSEA TV Company _Black Sea_ Ltd,UA 31593 UA ripencc
2014-07-11 01:49:53-05 46.149.179.87 46.149.179.0/24 ISP-KIM-NET Kalush Information Network LTD,UA 197522 UA ripencc
2014-07-11 01:49:53-05 82.112.53.75 82.112.32.0/19 KTEL-AS K Telecom Ltd.,RU 48642 RU ripencc
2014-07-11 01:49:53-05 95.133.181.160 95.133.128.0/18 UKRTELNET JSC UKRTELECOM,UA 6849 UA ripencc
2014-07-11 01:49:53-05 109.86.112.170 109.86.112.0/22 BANKINFORM-AS TOV _Bank-Inform_,UA 13188 UA ripencc
2014-07-11 01:49:53-05 124.197.73.68 124.197.64.0/18 MOBILEONELTD-AS-AP MobileOne Ltd. Mobile/Internet Service Provider Singapore,SG 4773 SG apnic
2014-07-11 01:49:54-05 178.137.97.155 178.137.0.0/17 KSNET-AS _Kyivstar_ PJSC,UA 15895 UA ripencc
2014-07-11 01:49:54-05 217.112.220.202 217.112.208.0/20 TELEPORTSV PrivateJSC DataGroup,UA 15785 UA ripencc
2014-07-11 02:08:05-05 94.76.127.113 94.76.127.0/24 FREENET-AS Freenet Ltd.,UA 31148 UA ripencc
2014-07-11 02:08:05-05 213.231.6.9 213.231.0.0/18 BREEZE-NETWORK TOV TRK _Briz_,UA 34661 UA ripencc
2014-07-11 02:08:05-05 37.57.203.171 37.57.200.0/21 BANKINFORM-AS TOV _Bank-Inform_,UA 13188 UA ripencc
2014-07-11 02:29:13-05 31.40.33.46 31.40.32.0/19 GORSET-AS Gorodskaya Set Ltd.,RU 49776 RU ripencc
2014-07-11 02:29:13-05 37.53.73.152 37.52.0.0/14 6849 6877 UA ripencc
2014-07-11 02:29:14-05 46.119.213.230 46.119.0.0/16 KSNET-AS _Kyivstar_ PJSC,UA 15895 UA ripencc
2014-07-11 02:29:14-05 46.175.73.188 46.175.64.0/20 MEDIANA-AS Mediana ltd.,UA 56347 UA ripencc
2014-07-11 02:29:14-05 176.73.87.120 176.73.0.0/17 CAUCASUS-CABLE-SYSTEM Caucasus Online Ltd.,GE 20771 GE ripencc
2014-07-11 02:29:14-05 178.219.91.40 178.219.90.0/23 ASDNEPRONET Dnepronet Ltd.,UA 51069 UA ripencc
2014-07-11 02:29:14-05 185.14.102.108 185.14.102.0/24 ORBITA-PLUS-AS ORBITA-PLUS Autonomous System,KZ 21299 KZ ripencc
2014-07-11 02:29:14-05 195.225.147.101 195.225.144.0/22 UA-LINK-AS NPF LINK Ltd.,UA 34359 UA ripencc
2014-07-11 02:50:03-05 46.150.74.97 46.150.64.0/19 VIVANET-AS Vivanet Ltd,UA 44728 UA ripencc
2014-07-11 02:50:04-05 46.150.91.162 46.150.64.0/19 VIVANET-AS Vivanet Ltd,UA 44728 UA ripencc
2014-07-11 02:50:04-05 76.14.215.195 76.14.192.0/18 WAVE-CABLE - Wave Broadband,US 32107 US arin
2014-07-11 02:50:04-05 82.193.220.254 82.193.192.0/19 VODATEL-AS Metronet telekomunikacije d.d.,HR 25528 HR ripencc
2014-07-11 02:50:04-05 178.136.227.61 178.136.226.0/23 ALKAR-AS PRIVATE JOINT-STOCK COMPANY _FARLEP-INVEST_,RU 6703 UA ripencc
2014-07-11 02:50:04-05 178.137.69.209 178.137.0.0/17 KSNET-AS _Kyivstar_ PJSC,UA 15895 UA ripencc
2014-07-11 02:50:04-05 194.28.176.201 194.28.176.0/22 KUZNETSOVSK-AS FOP Chaika Nadija Jakivna,UA 197073 UA ripencc
2014-07-11 02:50:04-05 212.87.183.197 212.87.160.0/19 EDN-AS Online Technologies LTD,UA 45025 UA ripencc
2014-07-11 02:50:04-05 213.231.12.80 213.231.0.0/18 BREEZE-NETWORK TOV TRK _Briz_,UA 34661 UA ripencc
2014-07-11 02:50:04-05 46.119.175.13 46.119.0.0/16 KSNET-AS _Kyivstar_ PJSC,UA 15895 UA ripencc
2014-07-11 03:09:01-05 46.33.50.175 46.33.48.0/21 LIS Telecompany LiS LTD,UA 35588 UA ripencc
2014-07-11 03:09:04-05 46.98.237.27 46.98.0.0/16 FREGAT-AS ISP _Fregat_ Ltd.,UA 15377 UA ripencc
2014-07-11 03:09:04-05 46.185.73.100 46.185.64.0/18 KSNET-AS _Kyivstar_ PJSC,UA 15895 UA ripencc
2014-07-11 03:09:04-05 79.164.171.236 79.164.0.0/16 CNT-AS OJSC Central telegraph,RU 8615 RU ripencc
2014-07-11 03:09:04-05 91.244.137.151 91.244.128.0/20 PERVOMAYSK-AS PP _SKS-Pervomaysk_,UA 44798 UA ripencc
2014-07-11 03:09:05-05 109.86.234.51 109.86.232.0/21 BANKINFORM-AS TOV _Bank-Inform_,UA 13188 UA ripencc
2014-07-11 03:09:05-05 109.207.121.193 109.207.112.0/20 TELELAN-AS Teleradiocompany TeleLan LLC,UA 196740 UA ripencc
2014-07-11 03:09:05-05 176.108.235.203 176.108.232.0/22 SKM-AS PE Yaremenko O.V.,UA 39422 UA ripencc
2014-07-11 03:09:05-05 193.106.82.45 193.106.80.0/22 DATAGROUP PRIVATE JOINT STOCK COMPANY _DATAGROUP_,UA 21219 UA ripencc
2014-07-11 03:09:05-05 31.129.65.152 31.129.64.0/19 ASDNEPRONET Dnepronet Ltd.,UA 51069 UA ripencc
2014-07-11 03:09:05-05 37.232.181.13 37.232.160.0/19 INTERNET-CENTER-AS Net By Net Holding LLC,RU 42420 RU ripencc
2014-07-11 03:29:59-05 109.201.240.84 109.201.224.0/19 VOLIA-AS Kyivski Telekomunikatsiyni Merezhi LLC,UA 25229 UA ripencc
2014-07-11 03:30:00-05 141.101.11.69 141.101.0.0/19 WILDPARK-AS ISP WildPark, Ukraine, Nikolaev,UA 31272 UA ripencc
2014-07-11 03:30:00-05 188.230.1.99 188.230.0.0/21 ABUA-AS LLC AB Ukraine,UA 43266 UA ripencc
2014-07-11 03:30:01-05 46.119.134.13 46.118.0.0/15 KSNET-AS _Kyivstar_ PJSC,UA 15895 UA ripencc
2014-07-11 03:30:01-05 77.79.140.237 77.79.128.0/18 UBN-AS OJSC _Ufanet_,RU 24955 RU ripencc
2014-07-11 03:30:01-05 77.121.125.112 77.121.96.0/19 VOLIA-AS Kyivski Telekomunikatsiyni Merezhi LLC,UA 25229 UA ripencc
2014-07-11 03:30:01-05 77.123.241.141 77.123.224.0/19 IVC IVC-Donbass Ltd,UA 48169 UA ripencc
2014-07-11 03:48:03-05 213.231.4.163 213.231.0.0/18 BREEZE-NETWORK TOV TRK _Briz_,UA 34661 UA ripencc
2014-07-11 03:48:03-05 5.248.133.146 5.248.0.0/16 KSNET-AS _Kyivstar_ PJSC,UA 15895 UA ripencc
2014-07-11 03:48:03-05 81.163.136.160 81.163.128.0/19 DIDAN-AS Didan Group LTD,UA 47694 UA ripencc
2014-07-11 03:48:03-05 91.244.232.200 91.244.232.0/22 VITA-AS Teleradiokompaniya Vizit-A Limited Liability Company,UA 197175 UA ripencc
2014-07-11 03:48:03-05 176.112.17.229 176.112.0.0/19 MAINSTREAM-AS PP MainStream,UA 44924 UA ripencc
2014-07-11 03:48:03-05 176.124.1.31 176.124.0.0/19 DIDAN-AS Didan Group LTD,UA 47694 UA ripencc
2014-07-11 03:48:03-05 193.93.238.13 193.93.236.0/22 STAVSET-AS Kvartal Plus Ltd,RU 49325 RU ripencc
2014-07-11 04:09:03-05 46.118.136.44 46.118.0.0/16 KSNET-AS _Kyivstar_ PJSC,UA 15895 UA ripencc
2014-07-11 04:09:05-05 46.172.128.249 46.172.128.0/19 UTEAM-AS Uteam LTD,UA 49125 UA ripencc
2014-07-11 04:09:05-05 94.41.219.215 94.41.192.0/18 UBN-AS OJSC _Ufanet_,RU 24955 RU ripencc
2014-07-11 04:09:05-05 109.162.59.249 109.162.0.0/18 KSNET-AS _Kyivstar_ PJSC,UA 15895 UA ripencc
2014-07-11 04:09:05-05 178.45.188.246 178.45.160.0/19 OJSC Rostelecom,RU 15500 RU ripencc
2014-07-11 04:09:05-05 178.88.215.41 178.88.0.0/16 KAZTELECOM-AS JSC Kazakhtelecom,KZ 9198 KZ ripencc
2014-07-11 04:09:05-05 188.163.29.68 188.163.0.0/17 KSNET-AS _Kyivstar_ PJSC,UA 15895 UA ripencc
2014-07-11 04:09:05-05 5.14.25.76 5.12.0.0/14 RCS-RDS RCS & RDS SA,RO 8708 RO ripencc
2014-07-11 04:09:05-05 5.248.99.163 5.248.0.0/16 KSNET-AS _Kyivstar_ PJSC,UA 15895 UA ripencc
2014-07-11 04:27:48-05 178.151.23.241 178.151.22.0/23 BANKINFORM-AS TOV _Bank-Inform_,UA 13188 UA ripencc
2014-07-11 04:27:50-05 31.169.23.129 31.169.20.0/22 DTVKZ-AS JSC Kazakhtelecom,KZ 39725 KZ ripencc
2014-07-11 04:27:50-05 77.122.235.167 77.122.192.0/18 VOLIA-AS Kyivski Telekomunikatsiyni Merezhi LLC,UA 25229 UA ripencc
2014-07-11 04:27:50-05 78.62.94.153 78.62.80.0/20 TEOLTAB TEO LT AB Autonomous System,LT 8764 LT ripencc
2014-07-11 04:27:50-05 89.209.96.231 89.209.0.0/16 MTS MTS OJSC,RU 8359 UA ripencc
2014-07-11 04:27:50-05 93.79.143.194 93.79.128.0/17 VOLIA-AS Kyivski Telekomunikatsiyni Merezhi LLC,UA 25229 UA ripencc
2014-07-11 04:27:50-05 176.8.79.228 176.8.0.0/16 KSNET-AS _Kyivstar_ PJSC,UA 15895 UA ripencc
2014-07-11 04:27:50-05 178.141.98.171 178.141.0.0/16 MTS-KRV-AS MTS OJSC,RU 44677 RU ripencc
2014-07-11 04:49:18-05 176.113.146.32 176.113.144.0/20 BELICOM-AS FOP Bilenkiy Olexander Naumovich,UA 44010 UA ripencc
2014-07-11 04:49:21-05 178.137.109.91 178.137.0.0/17 KSNET-AS _Kyivstar_ PJSC,UA 15895 UA ripencc
2014-07-11 04:49:21-05 213.111.226.174 213.111.192.0/18 MAINSTREAM-AS PP MainStream,UA 44924 UA ripencc
2014-07-11 04:49:21-05 217.73.84.131 217.73.80.0/21 INFOMIR-NET Infomir JSC,UA 44291 UA ripencc
2014-07-11 04:49:21-05 5.20.162.237 5.20.160.0/19 CGATES-AS UAB _Cgates_,LT 21412 LT ripencc
2014-07-11 04:49:21-05 5.105.1.241 5.105.0.0/16 CDS-AS Cifrovye Dispetcherskie Sistemy,UA 43554 UA ripencc
2014-07-11 04:49:21-05 77.122.193.42 77.122.192.0/18 VOLIA-AS Kyivski Telekomunikatsiyni Merezhi LLC,UA 25229 UA ripencc
2014-07-11 04:49:21-05 91.225.162.98 91.225.160.0/22 ASSPDCHERNEGA SPD Chernega Aleksandr Anatolevich,UA 56400 UA ripencc
2014-07-11 04:49:21-05 91.236.249.33 91.236.248.0/22 SNAK-AS IP-Connect LLC,UA 57944 UA ripencc
2014-07-11 04:49:21-05 91.244.139.49 91.244.128.0/20 PERVOMAYSK-AS PP _SKS-Pervomaysk_,UA 44798 UA ripencc
2014-07-11 04:49:21-05 109.86.76.58 109.86.64.0/20 BANKINFORM-AS TOV _Bank-Inform_,UA 13188 UA ripencc
2014-07-11 04:49:21-05 176.36.67.204 176.36.0.0/14 LANETUA-AS Lanet Network Ltd.,UA 39608 UA ripencc
2014-07-11 05:08:15-05 46.46.96.199 46.46.64.0/18 FLAGMAN-AS TOV _Flagman Telecom_,UA 48045 UA ripencc
2014-07-11 05:08:16-05 46.149.178.203 46.149.176.0/20 ISP-KIM-NET Kalush Information Network LTD,UA 197522 UA ripencc
2014-07-11 05:08:16-05 95.37.213.26 95.37.128.0/17 NMTS-AS OJSC Rostelecom,RU 25405 RU ripencc
2014-07-11 05:08:16-05 178.251.109.168 178.251.104.0/21 DATALINE-AS Dataline LLC,UA 35297 UA ripencc
2014-07-11 05:08:17-05 31.41.128.57 31.41.128.0/21 ANOXIN FIZICHNA OSOBA-PIDPRIEMEC ANOHIN IGOR VALENTINOVICH,UA 39056 UA ripencc
2014-07-11 05:27:32-05 81.90.233.231 81.90.233.0/24 RADIOCOM-AS RadioCom ISP Autonomous System,UA 25071 UA ripencc
2014-07-11 05:27:32-05 81.162.70.217 81.162.64.0/20 GIGABYTE-AS Private Company Center for Development Information Technology _Gigabyte_,UA 198293 UA ripencc
2014-07-11 05:27:32-05 89.44.89.68 89.44.88.0/22 DNC-AS IM Data Network Communication SRL,MD 41053 RO ripencc
2014-07-11 05:27:32-05 91.244.148.241 91.244.144.0/21 PERVOMAYSK-AS PP _SKS-Pervomaysk_,UA 44798 UA ripencc
2014-07-11 05:27:32-05 188.168.94.122 188.168.0.0/16 TTK-RTL Closed Joint Stock Company TransTeleCom,RU 15774 RU ripencc
2014-07-11 05:27:32-05 62.80.161.77 62.80.160.0/19 INTERTELECOM-AS PJSC Inter-Telecom,UA 25386 UA ripencc
2014-07-11 05:30:03-05 198.105.254.240 198.105.254.0/24 SGINC - Search Guide Inc,US 36029 US arin
2014-07-11 05:30:03-05 198.105.244.240 198.105.244.0/24 SGINC - Search Guide Inc,US 36029 US arin

Wednesday, July 09, 2014

Roman Seleznev (AKA Bulba, AKA Track2, AKA NCUX) appears in US Court in Guam

The media is buzzing about the arrest of hacker and stolen credit card vendor Roman Seleznev who has appeared in court in the US territory of Guam after being arrested in the Maldives. We wrote about Seleznev as part of the RICO racketeering case against the owners and operators of the Carder.su website. (See The Carder.su indictment: United States v. Kilobit et. al.) but that was only the first part of Seleznev's trouble. Until this weekend, the original 27-page indictment against Seleznev in the Western District of Washington was under court seal.

In the Kilobit/Las Vegas indictment, the charges are that Seleznev did "Participate in a Racketeer Influenced Corrupt Organization [RICO]" and "Participated in a Conspiracy to Engage in a Racketeer Influenced Corrupt Organization."

The whole group are described in the indictment like this:

"The defendants herein, and others known and unknown, are members of, employed by, and associates of a criminal organization, hereafter referred to as "the Carder.su organization," whose members engage in acts of identity theft and financial fraud, including, but not limited to, acts involving trafficking in stolen means of identification; trafficking in, production and use of couterfeit identification documents; identity theft; trafficking in, production and use of unauthorized and counterfeit access devices; and bank fraud; and whose members interfere with interstate and foreign commerce through acts of identity theft and financial fraud. Members and associates of the Carder.su organization operate principally in Las Vegas, Nevada, and elsewhere.

The important thing to understand about RICO is that as PART OF THE CORRUPT ORGANIZATION all of the charged members are sentenced as if the whole group did all of the crimes.

What does that mean to Seleznev? In Las Vegas, Nevada, Seleznev is being charged with being part of a RICO group that is credited with directly causing, in actual measured and aggregated fraudulent transaction losses, $50,893,166.35!!

But before Vegas gets their hands on him, Seleznev will face charges in the Western District of Washington for Case # 2:11-cr-0070-RAJ-1.

In that case, Roman Seleznev, AKA TRACK2, AKA Roman Ivanov, AKA Ruben Samvelich, AKA nCuX, AKA Bulba, AKA bandysli64, AKA smaus, AKA Zagreb, AKA shmak is charged with:

(Counts 1-5) Bank Fraud 18:1344 & 2
(6-13)  Intentional Damage to a Protected Computer 18:1030(a)(5)(A) & 1030(c)(4)(B)(i) & 2
(14-21) Obtaining InformationFrom a Protected Computer 18:1030(a)(2) & 1030(c)(2)(ii) & 2
(22) Possession of Fifteen or More Unauthorized Access Devices 18:1029(a)(3) & 1029(c)(1)(A)(i) & 2 
(23-24) Trafficking in Unauthorized Access Devices 18:1029(a)(2) & 1029(c)(1)(A)(i) & 2  
(25-29) Aggravated Identity Theft 18:1028(a)(1) & 2
This 27 page indictment, filed March 3, 2011, was just unsealed on July 6, 2014 when Seleznev appeared in court in Guam.

Washington charges that Seleznev "knowingly and willfully devised and executed and aided and abetted a scheme and artifice to defraud various financial institutions, including, but not limited to, Boeing Employees' Credit Union, Chase Bank, Capital One, Citibank, and Keybank, and to obtain moneys, funds, and credits under the custody and control of the banks by means of material false and fraudulent pretenses, representations and promises, as further described below."

Seleznev would:

  1. hack into retail businesses,
  2. install malicious computer code onto those hacked computers,
  3. and use the malware to steal credit card numbers from the victim businesses' customers
  4. market and sell the stolen credit card numbers on "criminally inspired" websites
  5. thus allowing these cards and the associated accounts to be used for fraudulent purposes by the customers of his service.
Seleznev's malware primarily was controlled from a server named shmak.fvds.ru or smaus.fvds.ru at the IP address 188.120.225.66 which is housed in a data center in the Russian Federation of Irkutsk. (That IP-name mapping is confirmed by Internet Identity's historical Passive DNS systems in May 2010.) A collection of malware found at the root site of that website, including malware named shmak, shmak2, kameo, hameo, zameo, dtc, dtc2, dtc4, rsca, remcomsvc, and others. FVDS.RU is a "third level domain" system that is attractive to criminals wishing to host malware on dedicated hostnames, without having to have their ownership of the hostname tracked in WHOIS services or through credit card payments.

Seleznev's websites for selling cards were primarily bulba.cc, secure.bulba.cc, Track2.name, and secure.Track2.name.

The targeted businesses usually had several "point of sale" terminals "up front" and a "back of the house computer" which may have been a server or perhaps even just the manager's computer.

Some of Seleznov's victims included:

The Broadway Grill - 32,000 unique credit card numbers from Dec 1, 2009 to Oct 22, 2010

Grand Central Baking Company in Seattle, WA

four Mad Pizza restaurants (three in Seattle, one in Tukwila, WA)

Village Pizza in Anacortes, WA

Casa Mia Italian in Yelm, WA.

Schlotsky's Deli in Coeur d'Alene, Idaho

Active Networks in Frostburg, MD

Days Jewelry in Waterville, Maine

Latitude Bar and Grill, NY, NY

Mary's Pizza Shack in Sonoma, CA

City News Stand in Chicago and Evanston, IL

Bulba would advertise when he had new cards for sale, claiming as many as 17,000 "Fresh Dumps" (newly stolen and never before used for fraud) cards and offering guarantees, including free card replacement for cards that were declined. Seleznev/Bulba had such high quality, that the owners of the popular crdsu.su and carder.biz allowed Seleznev and others to assume Monopoly status as the preferred card vendors for their boards, which were extremely prevalent in the underground.

According to the newly unsealed indictment, Seleznev personally stole (through his malware) more than 200,000 cards, and succesfully sold over 140,000 of those cards through his websites bulba.cc and Track2.name between November 15, 2010 and February 22, 2011, generating direct illicit profits in excess of $2,000,000 USD.

Just the cards stolen by Seleznev at the Broadway Grill have been associated with $79,317 in fraudulent charges, and all of the cards stolen by Seleznev are responsible for actual fraud charges of at least $1,175,217.37.

November 15-16, 2010, $83,490 in charges were made against Boeing Employees Credit Union cards.

Jan 31-Feb 1, 2011, $30,716 in charges against BECU.

Seleznev will have a hearing in Guam on July 22, and then be transferred to the Seattle courts.

Seleznev Diplomatic Spat with Russia?

The story is growing into an international diplomatic spat as a Russian politician and member of the Duma, Valery Seleznev, is the father of the cyber criminal. In a statement from the Russian Foreign Ministry, the Russians accuse Maldives of ignoring their Bilateral Treaty of 1999 on Mutual Assistance in Criminal Matters. The statement says this is the third recent case of a similar situation, citing the examples of Viktor Bout and K.V. Yaroshenko as other recent cases where the US has forcibly taken a Russian citizen from a third country to stand trial in the United States. I strongly agree with the statement at the close of their statement, where they "strongly encourage our countryment to pay attention to the cautions posted by the Russian Foreign Ministry on their website about the risks associated with foreign travel, if there is a suspicion that U.S. law enforcement agencies can charge them with any crime."

Who are these others who are mentioned? Viktor Bout (Виктор Анатольевич Бут) was arrested in Thailand in 2008 and extradited in 2010 to stand trial for terrorism charges for delivering anti-aircraft missiles to FARC in Colombia. He was convicted by a jury in Manhattan (More from The Guardian) Konstantin Yaroshenko was arrested in May 2010 in Liberia as a cocaine smuggler pilot when he landed his plane in Monrovia, Liberia and was arrested by the DEA as he tried to negotiate a contract for $4.5 million to deliver 5 tons of cocaine from Colombia to West Africa. Yaroshenko was knowingly working with smugglers who were raising funds for the Colombian terror group FARC. (See Superseding Indictment

Tuesday, July 08, 2014

E-ZPass Spam leads to Location Aware Malware

Jump to bottom for update list of malicious URLs

If you drive in a city with toll roads, you are familiar with the E-Z Pass System. If you are, you may have been tempted to click on an email that looked like this:
A quick search in the Malcovery Security Spam Data Mine revealed these related emails:

    date    |                subject                |           sender_name           
------------+---------------------------------------+---------------------------------
 2014-07-08 | In arrears for driving on toll road   | E-ZPass Collection Agency
 2014-07-08 | In arrears for driving on toll road   | E-ZPass Info
 2014-07-08 | In arrears for driving on toll road   | E-ZPass Customer Service Center
 2014-07-08 | In arrears for driving on toll road   | E-ZPass Info
 2014-07-08 | Indebted for driving on toll road     | E-ZPass Service Center
 2014-07-08 | Indebted for driving on toll road     | E-ZPass Service Center
 2014-07-08 | Indebted for driving on toll road     | E-ZPass Collection Agency
 2014-07-08 | Indebted for driving on toll road     | E-ZPass Customer Service Center
 2014-07-08 | Indebted for driving on toll road     | E-ZPass Info
 2014-07-08 | Indebtedness for driving on toll road | E-ZPass Collection Agency
 2014-07-08 | Indebtedness for driving on toll road | E-ZPass Customer Service Center
 2014-07-08 | Indebtedness for driving on toll road | E-ZPass Customer Service Center
 2014-07-08 | Pay for driving on toll road          | E-ZPass Info
 2014-07-08 | Payment for driving on toll road      | E-ZPass Info
 2014-07-08 | Payment for driving on toll road      | E-ZPass Info
 2014-07-08 | Payment for driving on toll road      | E-ZPass Info
But the destination websites are certainly not on E-Z Pass's domains!
          machine          |                               path                                
---------------------------+-------------------------------------------------------------------
 www.federalparts.com.ar   | /tmp/api/3eLv aFKXBvmuxydKFVfEZIMWSl7f4VJfOpfcdAHPeo=/toll
 www.fiestasnightclub.com  | /tmp/api/kJ1a5XRhE7MM9YhRVR1186why1TgPCPH7aieECyjb I=/toll
 www.flavazstylingteam.com | /tmp/api/vBrLdEDWRK4sXs6KaHEbWzHnbEYIFSo42BZvGd4crCY=/toll
 www.fleavalley.com        | /tmp/api/ycI2IRHcInDd1/cetyLMZMjwyxKxTAEHFkjk1dRUfYs=/toll
 www.frazeryorke.com       | /wp-content/api/LtvaZdAvP3GFuaqyulY/C3haFCeID3krbtMHt52cdnM=/toll
 www.fsp-ugthuelva.org     | /tmp/api/fMVyiIXcbY9gamr17zPrnhTgz2Zvs825GTmvvRjlTIA=/toll
 www.fyaudit.eu            | /components/api/yiBOsvUdvftbCd4Fa1zmVtIkbs4x3ThiUnFoIgwyI9Q=/toll
 www.giedrowicz.pl         | /tmp/api/R4a4iKmACUtWoRHq1DsCiQ1aH 3J7QgBMfp1zq8gqj8=/toll
 www.gostudy.ca            | /components/api/Q/sV7HtfnZGOW4lzlLSfFuKM/lLu8LQmOlT TVXKb2o=/toll
 www.graphiktec.com        | /tmp/api/nZbX6I6vYQrsTlY4OAw44Qq96Lnw/JOoLDdBmdLh21M=/toll
 www.h2oasisinc.com        | /components/api/BivlBt/AhVodCMM9zRuvcQpIyG2X6Knd8sERnP1 QDA=/toll
 www.habicher.eu           | /tmp/api/yra96tiDlyYbYxsbJpr/hDVSPmwh6GKYLF6PaD3nUAI=/toll
 www.grupoancon.com        | /components/api/6jI99hwDmjAvkEvuX8JvVSkS3InPtLii ZN3dbIVkOM=/toll
 www.happymaree.com.au     | /tmp/api/d4ik5Y2GvCVSSJQhXI9wYYpBvxjLS78peeRYMKV0V7c=/toll
 www.headspokerfest.com    | /tmp/api/RTuPCuYLjaj1KnTeJrMlCoH9HL4IixR eBvajB6TCeE=/toll
 www.headspokerfest.com    | /tmp/api/43J6l5G/CkNp6kmGl0b jUY/oOL4411pPds8nylDE5g=/toll
When we visit one of the URLs, we are prompted to download a .zip file, containing a .exe file.

Both are conveniently named for the City and ZIP Code from which we are connected.

For example:

When we run this malware, it attempts to make contact with the following C&C locations:

76.74.184.127:443
113.53.247.147:443
50.57.139.41:8080
188.165.192.116:8080
82.150.199.140:8080
203.157.142.2:8080
212.45.17.15:8080
92.240.232.232:443
188.165.192.116:8080
At Malcovery Security, we've been tracking the ASProx botnet for some time. Most of these IP addresses were already known to belong to the ASProx botnet for some time. This is the same botnet that sent the Holiday Delivery Failure spam imitating Walmart, CostCo, and BestBuy over the holidays and that send the Court Related Malware through the early months of 2014.

Thanks to some updates from new friends on Twitter, we wanted to give an update on what we are seeing in the Malcovery Spam Data Mine. Because every advertised URL is unique, we have taken the approach of replacing the "unique stuff" with "...STUFF..." in the URLs below. The important part is that we realize that anything that you see in your logs that includes either "tmp/api" or "wp-content/api" or "components/api" and then some "STUFF" and then "=/toll" is going to be one of these URLs that is part of the current E-Z Pass spam, which began on July 8th and is still continuing here on July 12th. If you have access to Very Large Logs, we'd love to get YOUR URLs of this pattern to see if we can help webmasters identify and shut this stuff down. Note the alphabetical progression through compromised domain names? These are sorted by timestamp, not by domain name. It just so happens those are the same thing. We believe the criminals have a very large list of pre-compromised domains that they can use at will. Possibly these are just harvested passwords from other malware campaigns.

This malware is the ASProx malware. If anyone has more details on the "what happens next?" part of the malware, please do share. What we have observed and been told is that infected machines are primarily used for advertising click-fraud, but happy to learn more about those aspects and share what we learn.

2014-07-08 10:15:00-05 www.fiestasnightclub.com "/tmp/api/..STUFF…=/toll
2014-07-08 11:15:00-05 www.flavazstylingteam.com "/tmp/api/..STUFF…=/toll
2014-07-08 11:20:00-05 www.fleavalley.com "/tmp/api/..STUFF…=/toll
2014-07-08 13:20:00-05 www.fsp-ugthuelva.org "/tmp/api/..STUFF…=/toll
2014-07-08 13:30:00-05 www.frazeryorke.com "/wp-content/api/…STUFF…=/toll
2014-07-08 14:10:00-05 www.fyaudit.eu "/components/api/…STUFF…=/toll
2014-07-08 15:30:00-05 www.giedrowicz.pl "/tmp/api/..STUFF…=/toll
2014-07-08 16:40:00-05 www.gostudy.ca "/components/api/…STUFF…=/toll
2014-07-08 17:45:00-05 www.graphiktec.com "/tmp/api/..STUFF…=/toll
2014-07-08 18:45:00-05 www.h2oasisinc.com "/components/api/…STUFF…=/toll
2014-07-08 18:50:00-05 www.habicher.eu "/tmp/api/..STUFF…=/toll
2014-07-08 19:00:00-05 www.grupoancon.com "/components/api/…STUFF…=/toll
2014-07-08 19:20:00-05 www.headspokerfest.com "/tmp/api/..STUFF…=/toll
2014-07-08 19:30:00-05 www.happymaree.com.au "/tmp/api/..STUFF…=/toll
2014-07-09 01:10:00-05 www.ingersollpharmasave.ca "/components/api/…STUFF…=/toll
2014-07-09 01:30:00-05 www.improlabsa.com "/components/api/…STUFF…=/toll
2014-07-09 01:45:00-05 www.innovem.nl "/components/api/…STUFF…=/toll
2014-07-09 02:00:00-05 www.intelliwaste.net "/components/api/…STUFF…=/toll
2014-07-09 04:15:00-05 www.investment-mastery.com "/wp-content/api/…STUFF…=/toll
2014-07-09 05:50:00-05 www.islandbiblechapel.com "/tmp/api/..STUFF…=/toll
2014-07-09 06:15:00-05 www.ironstoneranch.com "/tmp/api/..STUFF…=/toll
2014-07-09 13:00:00-05 www.klaafalaaf.de "/components/api/…STUFF…=/toll
2014-07-09 20:00:00-05 www.listerus-capital.com "/components/api/…STUFF…=/toll
2014-07-10 00:10:00-05 www.learn-a-language.eu "/components/api/…STUFF…=/toll
2014-07-10 06:30:00-05 www.mindsolutions.sk "/components/api/…STUFF…=/toll
2014-07-10 07:15:00-05 www.mintom.it "/components/api/…STUFF…=/toll
2014-07-10 14:00:00-05 www.moretrends.de "/tmp/api/..STUFF…=/toll
2014-07-10 15:00:00-05 www.nortech.com.au "/components/api/…STUFF…=/toll
2014-07-10 18:30:00-05 www.p-press.com "/components/api/…STUFF…=/toll
2014-07-11 00:00:00-05 www.porno-sexshop.ch "/tmp/api/..STUFF…=/toll
2014-07-11 01:00:00-05 www.powiatstargardzki.eu "/components/api/…STUFF…=/toll
2014-07-11 02:00:00-05 www.projectstc.org "/components/api/…STUFF…=/toll
2014-07-11 08:15:00-05 www.radmotors.com.pl "/components/api/…STUFF…=/toll
2014-07-11 10:10:00-05 www.reportsolutions.com "/components/api/…STUFF…=/toll
2014-07-11 16:00:00-05 www.search4staff.com "/components/api/…STUFF…=/toll
2014-07-11 18:00:00-05 www.sirman.us "/tmp/api/..STUFF…=/toll
2014-07-11 20:30:00-05 www.stjosephbristol.org "/components/api/…STUFF…=/toll
2014-07-11 21:15:00-05 www.stpat.nsw.edu.au "/components/api/…STUFF…=/toll
2014-07-12 15:00:00-05 avauncemarketing.net "/wp-content/api/…STUFF…=/toll

Disk57.com, Cutwail, and Tearing Down Offending Infrastructure

Sometimes I am so impressed by the things my employees at Malcovery discover as they work through the various email-based threats we process and report about for our customers. Brendan, Wayne, and J evaluate and document hundreds of malware threats each week from our Spam Data Mine and because of their daily interactions with so much malware notice patterns that others miss. I've been asking them to be especially mindful of what the Cutwail spammers are moving to next as the GameOver Zeus era moves to a close, and Brendan did a great job of covering that over on the Malcovery Blog in the article How Spammers Are Filling the Gameover Zeus Void.

June 16 - Disk57.com first sighted

On June 16, 2014, Brendan and the team noticed three malware campaigns distribution spam campaigns that were all pushing the same malware. The email subjects were:

Subject: USPS - Missed package delivery
Subject: You have received a new fax
Subject: Scanned Image from a Xerox WorkCentre

The files attached to those messages included:

USPS1758369.zip - (22,331 bytes) - MD5: 73c4758a84c4a0e24e4f34db69584d26
(VirusTotal results at report time: 3/54)

Scan.zip - (22,329 bytes) - MD5: cbfb3f1e40b30d01f4dda656d7f576e7
(VirusTotal results at report time: 3/54)

IncomingFax.zip - 22,329 bytes - MD5: 048dcc8c9639d2e8ccea362fdb5f7d3e
(VirusTotal results at report time: 3/54)

All three of those .zip files contained the same binary, with the varying names, USPS06162014.scr, Scan.scr, and IncomingFax.scr.

(40,960 bytes) - MD5: 36e264de2cb3321756a511f6c90510f5

(VirusTotal results at report time: 0/54)

By a week later, the detection rate was up to 38 of 46 AV products detecting this as malware, but at the time of the spam campaign, only Sophos and K7 had signature-based detection for the malware, though some vendors may have offered other types of protection.

Whichever of the three versions you downloaded, the SCR file was actually a PE-executable which would contact the site "disk57.com" in order to "check in" by hitting the file "gate.php" on that server. The Ukrainian server in question, 188.190.117.93, (AS197145, Kharkiv Infium LLC) had been seen previously communicating with malware on March 26 and March 27 using the domain name "malidini.com".

The registry was modified so that a copy of the .scr file (now named as an .exe) would be executed on the next start up due to a Policy statement located in "HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\policies\Explorer\Run\818107311"

This resulted in the downloaded of a 7200 byte ".mod" file

More Disk57.com sightings

Disk57.com was also used as part of the malware infrastructure for malware samples distributed by the following spam campaigns:

June 16 - Wells Fargo 
June 17 - USPS
June 18 - HSBC
June 18 - Xerox
June 18 - New Fax
June 30 - HSBC - Subject: Avis de Paiement
June 30 - New Fax - Subject: You have received a new fax message
June 30 - Scanned Document - Subject: Scan de 
July 1 - BanquePopulaire
July 1 - French government
July 3 - Xerox
July 3 - UPS
July 3 - Wells Fargo
On June 30th, we saw the same technique used as in the June 16th campaigns. Three different .zip files, each containing a .scr file that was named differently, but where all samples had the same MD5 hash (MD5: 66dcf2e32aa902e2ffd4c06f5cb23b43 - VirusTotal detection 11/54 at report time.)

As on June 16th, executing the .scr file resulted in an exchange with the "gate.php" file on disk57.com on 188.190.117.93, resulting in a 7200 byte ".mod" file being downloaded.

On June 30th, however, this exchange resulted in a copy of the Cutwail binary, b02.exe, being downloaded from jasongraber.com on the path /css/b02.exe. (IP 192.64.181.14). b02.exe had a file size of 41,472 bytes - MD5: 84822121b11cce3c8a75f27c1493c6bb with a VirusTotal report of 2/54 at report time.

Upatre Updated

On July 3rd, spam campaigns imitating Xerox, UPS, and Wells Fargo used this same technique again with email subjects:

Subject: Scan from a Xerox WorkCentre - seen 1209 times by Malcovery
Subject: New Fax: # pages - seen 288 times by Malcovery
Subject: IMPORTANT - Confidential documents - seen 88 times by Malcovery
Subject: UPS - Credit Card Billing Adjustment. Ref#(random) - seen 178 times by Malcovery

1,941 messages were sent to our Spam Data Mine from 1,037 different sending IP addresses.

The .zip files still contained .scr files that were all the same
file size (23,040 bytes) MD5: 870c63c4420b6f187066a94ef6c56dc6 - VirusTotal report: 1/53 at report time.

However this time there were three very different URLs downloaded as a result of the initial click. The downloaded malware behaved almost exactly like the UPATRE samples that were used to distribute the encrypted version of GameOver Zeus that we wrote about back in February. (See: GameOver Zeus Now Uses Encryption to Bypass Perimeter Security.)

UPATRE Update

The UPATRE malware that was signature detected only by Sophos (as the useful name Mal/Generic-S) on July 3rd now has 43 detections at VirusTotal, although most are crap as usual, with regards to the usefulness of the names chosen by the vendors. Zbot.LDQ, Trojan/Win32.Zbot (but it clearly isn't Zeus, it's just a tiny downloader, which is what several vendors call it (Trojan.Win32.Tiny.bNKP). Several other vendors call it Ransomware or Crypto something or another (Trojan-Ransom.Win32.Cryptodef.oq, Win32/Ransom.ABOQAMB, TROJ_CRYPWALL.JER, Trojan.Win32.A.Cryptodef.23040). Only Microsoft called it Upatre (TrojanDownloader:Win32/Upatre.AA) although that is clearly the consensus of the AV analysts we have discussed the sample with. In this case the job of UPATRE is to download files that CLAIM to be PDF files, "convert/unpack/decrypt" them into .exe files, and then launch those .EXE files.

Three touches to the OVH (AS16276) IP address 94.23.247.202 resulted in three files so-called PDF files being downloaded from repele.net on IP address 82.220.34.132, each with the name "css/agreement.pdf". UPATRE did its magic, converting each of these files into another binary executable:

agreement.pdf = 131,173 bytes - MD5: 354283b80cc9e63d872475175d20f14d

(became CryptoWall Encryption ransomware, (in our case, named 09acd07.exe and located in a directory 09acd07 - 183,296 bytes - MD5: 6238af3e78f3316ea5f0192cb8cf3167 - VirusTotal reports detection of 14/53 at report time

which made connection to three C&C servers:
- vivatsaultppc.com - 194.58.101.96 in Russia (AS39134)
- bolizarsospos.com - 194.58.101.3 in Russia (AS39134)
- covermontislol.com - 31.31.204.59 in Russia (AS12695)

After encrypting files, the victim is shown the following text, with a timer counting down from 168 hours:

Your files are encrypted. To get the key to decrypt the files you have to pay 750 USD/EUR. If payment is not made before 10/07/14 - 15:37 the cost of decrypting files will increase 2 times and will be 1500 USD/EUR

(Other files found in that subdirectory included, DECRYPT_INSTRUCTION.HTML, DECRYPT_INSTRUCTION.TXT, and DECRYPT_INSTRUCTION.URL.)

agreement-2.pdf = 51,266 bytes - MD5: 06a16a7701c748467a0b8bc79feb7f35

(became Cutwail spamming botnet malware, mshvsk.exe (random file name) - 39,936 bytes - MD5: c1cc8b5eaf7f25449cfda0c6cd98b553 - VirusTotal reports detection of 1/54 at report time.

which then began communications to seven separate C&C servers:
- 91.217.90.125 in Russia (AS48031)
- 93.171.172.129 in Russia (AS29182)
- 93.170.104.81 in Netherlands (AS50245)
- 148.251.94.182 in Germany (AS24940)
- 91.237.198.93 in Russia (AS198681)
- 91.234.33.125 in Ukraine (AS56485)
- 91.221.36.184 in Russia (AS51724 - FLYNET)

agreement-3.pdf = 27,811 bytes - MD5: 19a1986f6fd0f243b02bba6cb77e9522

(became Andromeda botnet malware: gqxse.exe (random file name) - 23,150 bytes - MD5: 8e6c9e794739e67969c6f81a5786d9e7 VirusTotal reports detection of 0/54.

which then called out to disk57.com / gate.php)

What to do?

First and foremost, we need to get rid of Cutwail. This will be difficult as Russia continues to harbor their cyber criminals, allow them to bribe themselves out of prison and into government offices and contracts, and seems to treat their rampant theft of American and European wealth as a form of Economic Development.

In the meantime, we need to begin smashing their infrastructure at every chance we can get. Seize the hardware if we can, disable the routing of the traffic if we can't, and DEFINITELY block that infrastructure within our homes and companies!

Do yourself and your company a favor by sharing a link to this blog and recommending that your IT Security staff block the addresses shared above. If you live in a country where you can help, please do so!

Monday, June 30, 2014

Microsoft, njRat, and No-IP

Microsoft's Digital Crimes Unit is claiming their 10th major botnet action, this time targeting the malware known as Bladabindi, or more popularly njRAT, and Jenxcus, better known as H-worm. To do so, Microsoft filed a lawsuit in Nevada against three parties:

Naser Al Mutairi, a Kuwait City resident known to be the author of njRAT through his varias aliases, njq8, xnjq8x, njq8x, and njrat

Mohamed Benabdellah, an Algerian living in or near Mila, Algeria, who uses the aliases Houdini, houdinisc, and houdini-fx

and Vitalwerks Internet Solutions, LLC, d/b/a No-IP.com, with offices at 5905 South Virginia Street, Suite 200, Reno, Nevada 89502.

The lawsuit is also filed against "John Does 1-500" who are supposedly the 500 priniciple operators of njRAT and H-Worm malware. (H-Worm is a closely related RAT software, likely based off the same source code). Because they do not yet know the identities of these RAT operators, the are assigned "John Doe" aliases, in hopes that the power of discovery granted by the lawsuit can help to reveal their true identities.

On the other side of this Internet battle is Vitalwerks and their literally millions of service users. Vitalwerks provides the capability to host an Internet service despite the fact that your computer may be using DHCP-assigned IP address. Normally a webserver has to have a permanently assigned IP address which is listed by a DNS service so that computers on the Internet can find the service you are offering. With Dynamic DNS services, your computer can link to the service and constantly update its IP address so that even if your IP changes many times per day, your service users can find you. In Microsoft's lawsuit, they agree that "Dynamic DNS is a vital part of the Internet because it allows anyone to have a domain name even though they have a changing IP address." Their accusation is found in the next sentence, "However, if not properly managed, a Dynamic DNS service can be susceptible to abuse."

The lawsuit points out that in April 2013, OpenDNS published an article online detailing its investigation into Dynamic DNS abuse. In that study,On the Trail of Malicious Dynamic DNS Domains by my friend Dhia Mahjoub, OpenDNS collected resolutions of various Dynamic DNS domains, and concluded that during their study some domains, such as "hopto.org" were used for malicious purposes as often as 56% of the time! Other highly malicious URLs included:

hopto.org - 56.71%
us.to - 49.45%
myftp.org - 37.50%
myvnc.com - 33.33%
myftp.biz - 20.20%
dlinkddns.com - 12.22%
no-ip.info - 10.70%
no-ip.org - 4.57%
The lawsuit also discusses Symantec reporting about the malware being used on no-ip. One such Symantec report is: Simple njRAT fueld nascent middle east Cybercrime Scene. (Microsoft doesn't really mention that basically NOBODY calls the malware Bladabindi except Microsoft. Just call it njRAT like everyone else, please!) In that report, from March 2014, Symantec mentions one particular group that infects as many as 4500 computers per day using their C&C Servers at njratmoony.no-ip.biz and nrj.no-ip.biz.

This blogger confirmed the complaint firsthand that is made by No-IP themselves. Although Microsoft was supposedly going to ensure that "legitimate" no-ip customers were not impacted, for a significant part of the day on June 30, 2014, large portions of the Internet (including three linux servers that this blogger uses on three separate networks) had no idea how to find the no-ip domains. The nameservers were not propagated in such a way that the changes were seamless. No-IP's Formal Statement on Microsoft Takedown can be found on their website. In that statement, No-IP claims that "billions of queries" from "millions of innocent users" were dropped "because of Microsoft's attempt to remediate hostnames associated with a few bad actors" and implies that Microsoft did not dedicate enough resources to handle the traffic.

The primary purpose of the court orders was in fact to allow Microsoft to take matters into their own hands and filter the traffic for 130 pages worth (more than 18,000 3LDs) that were hosted by NO-IP and were associated with criminal activity and malware, primarily related to the two RATs, njRAT and H-Worm.

Of course on the other side of that is the fact that Microsoft documents that in the past twelve months MORE THAN SEVEN MILLION WINDOWS USERS were impacted by malware hosted on NO-IP domains! If someone's infrastructure is routinely abused to harm seven million of your customers, don't you have a right to do something about it? While NO-IP can claim that they have an active abuse desk that deals with these complaints, dozens of criminal tutorials would not recommend that you host your malware by setting up a NO-IP address, many of which have lived on consistent names for MANY MONTHS (as in the names mentioned in the above Symantec link) unless there was a clear pattern of NOT terminating offending 3LD (third level domains).

Cisco's fabulous cybercrime fighter, Levi Gundert, who I first worked with while he was working on the LA Electronic Crimes Task Force, as one of the most effective U.S. Secret Service cybercrime agents, and who later worked for Team Cymru, recently wrote a piece for Cisco's blog on Dynamic Detection of Malicious DDNS. Levi says that Free DDNS services "check all of the necessary attack boxes" that make the service desirable for criminals. As he explains:

Free DDNS services, by comparison, check all of the necessary attack boxes. Sub-domains can be quickly and easily generated and DNS records are trivially changed. For the remote access Trojan (RAT) crowd that are typically attempting to spy on female victims and running servers from home, DDNS is a natural fit. In fact, searching the web for tutorials on using freely available RATs like Black Shades, Dark Comet, or Poison Ivy returns results that all instruct RAT attackers to first create DDNS sub-domains in order to properly configure the RAT, specifically enabling a “back connect” to the attacker. Naturally, one segment of RAT users tend to be less technical, relying on tutorials and point and click interfaces to actually launch the RAT, which likely contributes significantly to the overall metrics of malicious DDNS use.

Levi provides this graph showing how often Cisco's Cloud Web Security blocks Dynamic DNS third level domains based on the reputation of that service in the following graph:


(source: blogs.cisco.com/security/dynamic-detection-of-malicious-ddns/ click image to enlarge )

zapto.org, one of the NO-IP domains, is blocked 100% of the time by users of Cisco's Cloud Web Service. no-ip.info, no-ip.org, and no-ip.biz are also all blocked between 50% and 100% of the time based on reputation. Levi next goes on to show of all the DDNS base domains, "what do the corresponding malware numbers look like for the DDNS domains most abused by threat actors?"


(source: blogs.cisco.com/security/dynamic-detection-of-malicious-ddns/ click image to enlarge )

Even after such widespread and published reports of NO-IP being used for malware abuse, Microsoft observed no significant change in their abuse practices, based on the malware analysis they performed. Following the February 2014 Cisco report, Microsoft "continues to see 2,000-3,000 new unique malware samples per month that are supported by No-IP."

But that doesn't mean No-IP is not responsive. Brian Krebs reported on this conflict in his article today Microsoft Darkens 4mm Sites in Malware Fight where he quotes No-IP's Natalie Gogun as saying that of the 18,000 sites mentioned in the Temporary Restraining Order, only about 2,000 of them were actually still live. Krebs quotes Crowdstrike's Dmitri Alperovitch mentioning that No-IP has always been very responsive, and I've seen the same. In fact, immediately following the Cisco blog above, a member of the No-IP security team was observed by this blogged on a security researcher mailing list asking if anyone could help him get the full list so he could make sure they killed all of the domain names mentioned. (Hi, Kurt!)

The problem here may be the nature of the malware used on these sites. While the security community regular sees and reports on financial crimes malware, such as Zeus, or malware that has significant and widespread distribution, in most cases njRat no-ip domains are being used by small-time botmasters to allow themselves to spy on a few dozen webcams. In fact, a review of more than 1800 recent URLs associated with delivering financial crimes malware observed by Malcovery Security's T3 product, NONE of the No-IP domains were seen to be used. Financial crime malware does not seem to be heavily associated with No-IP. While njRat certainly has the capability to be used for more significant crimes (including installing any additional malware desired by the criminals, and famously being used by the Syrian government to spy on the rebels) its primary reputation is as a tool for online perverts. Their typical victims tend to lack the Internet-savvy that allows corporate, industry, and government malware victims to report malware victimization to No-IP to receive a response. Sophisticated financial crimes malware criminals are very unlikely to link their malware back to dynamic DNS hosts that they personally control and are much more likely to use "more permanent" hosting in the form of hacked or leased servers.

The Microsoft complaint mentions YouTube, and we were able to quickly find many similar njRAT tutorials. There were also njRAT groups hosted on Facebook where botmasters were openly trading photographs of victims and offering to "trade slaves" (as they refer to the pretty girls whose webcams they control.) We reported three such groups to Facebook Security who took quick action to kill the groups which had a combined membership of more than 16,000 users!

Some examples of these creeps work might help illustrate the type of crimes committed by the typical njRat botmaster:

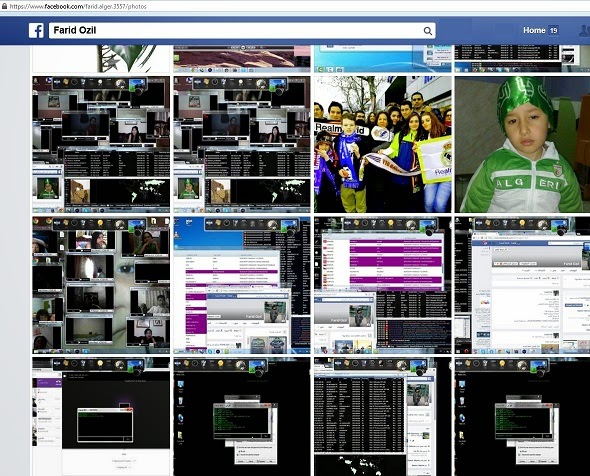
Farid shows a screenshot boasting of 200 simultaneously online njRAT victims.

Farid frequently posts photos of his conquests:

Others do the same:

Here's the Before and After of Farid's njrat group . . .

and after we reported the group to Facebook Security . . .

Conclusions?

I can't really take sides on this one. Do we need to do something more to help the victims of this kind of malware? Absolutely. Was it necessary to seize 22 domains at No-IP? I can't argue with Microsoft wanting to prevent infections to more than 7 million Windows victims, but I certainly can understand the great frustration experienced by the No-IP folks.

Thursday, June 05, 2014

Malcovery Examines GameOver Zeus

What is this graphic about? Read on, Gentle Reader!

Malcovery: Email Based Threat Intelligence and GameOver Zeus

At Malcovery Security we have become EXTREMELY familiar with GameOver Zeus. Our malware analysts create multiple reports each day documenting the top Email-based threats, and as the FBI's news releases (covered earlier this week in this blog, see Is it GameOver for GameOver Zeus? document, the criminals behind GameOver Zeus have been devastatingly thorough in compromising computers. Unlike some sandboxes, when Malcovery reports on a piece of malware, we actually report on "the activity that would result on a computer compromised by this malware" in a holistic view that we call Contextual Analysis. The goal of Malware Contextual Analysis is to help answer questions like:

  • How would one of my users likely be infected by this malware?
  • What email subjects or messages may have sent this malware?
  • Did that spam campaign deliver other malicious attachment or malicious URLs?
  • If one of my users were compromised by this malware, what network activity may result?
  • What additional malicious files might be downloaded by a computer compromised with this malware?
  • . . . and other questions, depending on the nature of the malware
Malcovery's main Malware Threat Intelligence analyst, Brendan Griffin, has shared a special report called The Many Faces of GameOver Zeus that examines many of the ways the malware has been delivered via spam campaigns. In this blog post, I'll be focusing on the Prominent IP addresses associated with the "Encrypted Drop" version of GameOver Zeus distribution.

GameOver Zeus's Encrypted Drop Sites

Back in February, Malcovery reported that GameOver Zeus was being prominently loaded by means of UPATRE malware downloading an Encrypted file from the Internet, and then executing that file. (See our post: GameOver Zeus Now Uses Encryption to Bypass Perimeter Security) With GameOver Zeus possibly taking a significant hit due to the coordinated law enforcement and researcher efforts, I wanted to look at the network infrastructure that we have been warning about in our T3 reports, and just illustrate how the T3 reports can be used to alert you to activity not just from the current day's malware, but for malware that touches any part of the extensive shared infrastructure of GameOver Zeus.

Since that initial post, we've seen GameOver Zeus-related encrypted files drop from more than 200 different internet locations, get decrypted by the Dropper malware, and execute themselves to begin communicating with the Peer to Peer GameOver Zeus infrastructure. The full list of many of those URLs, with the date on which we saw the spam campaign, the brand, item or company being imitated in that spam campaign, and the URLs where the GOZ binary were accessed, is available at the end of this article. Here is a sampling of some of the most recent ones for now to help understand the process...

2014-05-13 Xerox url::moraza.com.my/images/1305UKdp.zip
2014-05-13 NatWest url::luxesydiseno.com/images/powerslide/Concha/1305UKdw.zip
2014-05-14 Microsoft url::elpenterprisesinc.com/wp-content/uploads/2014/05/1405UKdw.enc
2014-05-14 Sage url::ballroom-intergalactica.com/wp-content/themes/twentythirteen/css/1405UKdp.enc
2014-05-14 Intuit url::mindinstitute.ro/Web3/Upload/Targ-rhc1405.dat
2014-05-14 NatWest url::jessicahann.co.uk/wp-content/uploads/2013/13/1405UKmp.enc
2014-05-14 ADP url::mindinstitute.ro/Web3/Upload/Targ-rhc1405.dat
2014-05-15 eFax url::factoryrush.com/test/1505UKmp.zip
2014-05-15 UK Ministry of Justice url::sugarlandrx.com/media/css/1505UKdp.zip
2014-05-15 eFax url::dubaimovers.info/scripts/Targ-1505USdp.tar
2014-05-15 Fidelity url::www.entrepreneurindia.com/css/Targ-1505USdp.tar
2014-05-15 Dun & Bradstreet url::dubaimovers.info/scripts/Targ-1505USdp.tar
2014-05-16 Bank of America url::kuukaarr01.com/wp-content/uploads/2014/05/Targ-1605USdp.tar
2014-05-19 Santander url::paperonotel.com/Scripts/heap170id2.exe
2014-05-19 Wells Fargo url::mersinprefabrik.com/Css/1905USmw.dct
2014-05-20 HSBC url::task-team.com/css/2005UKmw.zip
2014-05-20 NYC Govt url::lospomos.org/images/button/2005USmw.zip
2014-05-20 UPS url::alamx.com/images/RCH2005.zip
2014-05-20 UPS url::evedbonline.com/images/RCH2005.zip
2014-05-20 Royal Bank of Scotland url::lospomos.org/images/button/2005UKmw.zip
2014-05-20 LexisNexis url::evedbonline.com/images/RCH2005.zip
2014-05-21 Credit Agricole url::eleanormcm.com/css/2105UKdp.rar
2014-05-21 HSBC url::cedargrill.sg/css/2105UKdw.rar
2014-05-21 HSBC url::chezalexye.com/css/2105UKdw.rar
2014-05-21 JP Morgan url::footballmerch.com/media/css/Targ-2105USmw.tar
2014-05-27 Hewlett-Packard url::lotwatch.net/images/2705UKdp.rar
2014-05-27 Xerox url::auracinematics.com/acc/b02.exe
2014-05-29 Visa url::qadindunyasi.az/images/Targ-2905USmp.tar
2014-05-30 Sky url::3dparsian.com/images/banners/3005UKdp.rar
2014-05-30 HSBC url::bag-t.com/css/3005UKmw.rar
2014-05-30 HSBC url::seminarserver.com/html/3005UKmw.rar

For each of the campaigns above, Brendan, Wayne, and J, our malware analysis team, pushed out both an XML and STIX version of the machine readable T3 reports so that our customers could update themselves with information about the spam campaign, the IP addresses that sent that spam to us, the hashes of the spam attachment, the hostile URLs, and the IP addresses associated not only with the GameOver Zeus traffic, but whatever other malware was dropped in the same campaign. As the FBI indicated, it was extremely common for GameOver Zeus infected computers to ALSO become infected with CryptoLocker.

T3: Protection for Today and Tomorrow

But how often did we see "re-use" of network infrastructure? We like to say that Malcovery's T3 report, which stands for Today's Top Threat, is really "T3: Protection for Today and Tomorrow". To illustrate this, I did some data mining in Malcovery's Threat Intelligence database.

First - I isolated network activity for the 92 distinct spam campaigns illustrated above. (There were many more GameOver Zeus campaigns than that, but I was sticking to those samples that used the "encrypted file decrypted by the dropper" version that I had written about in February, so this is a sampling ...)

For each IP address that showed up in network traffic within those 92 campaigns, ranging from February 6, 2014 to May 30, 2014, I counted how many distinct campaigns that indicator had been seen in. Fifty-six IP addresses showed up in ten or more of those campaigns.

I took those IP addresses, and asked the Malcovery Threat Intelligence Database "which spam campaigns delivered malware that caused traffic to those IP addresses?" and was surprised to see not just the original 92 campaign I started with, but 360 distinct spam campaigns!! I culled that down by eliminating the campaigns that only touched ONE of those 56 IP addresses of high interest. The remaining 284 campaigns could be placed into 103 groups based on what they were imitating. Most of the top brands should be familiar to you from Malcovery's Top 10 Phished Brands That Your Anti-Virus is Missing report.

Brand Imitated in Spam# of Campaigns Seen
Ring Central 30 campaigns
HMRC 15 campaigns
HSBC 13 campaigns
Royal Bank of Scotland 14 campaigns
NatWest 11 campaigns
eFax 11 campaigns
Sage 10 campaigns
Lloyds Bank 8 campaigns
UK Government Gateway 8 campaigns
Xerox 8 campaigns
ADP 6 campaigns
Companies House 6 campaigns
IRS 6 campaigns
New Fax 5 campaigns
Paypal 5 campaigns
Sky 5 campaigns
UPS 5 campaigns
Amazon 4 campaigns
Bank of America 4 campaigns
BT.com 4 campaigns
Microsoft 4 campaigns
QuickBooks 4 campaigns
Wells Fargo 4 campaigns
WhatsApp 4 campaigns

I threw the data into IBM's i2 Analyst Notebook, my favorite tool for getting a quick visualization of data, and did some arrangement to try to show the regionality of the data. I know the graph is too dense to see what is in the interior, but let me explain it here:

On the left are IP addresses that are owned by Microsoft. They are arranged by Netblock, with the size of the Computer icon representing how many malware campaigns that IP was linked to. Top to bottom numerically by Netblock, these are from the 23.96 / 23.98 / 137.116, 137.135, 138.91, 168.61, 168.63, 191.232 blocks. The Microsoft traffic only started appearing in late April, so it is possible this is traffic related to "sinkholing" or attempting to enumerate the botnet as part of the investigation. I have no insider knowledge of any such activity, just stating what we observed. We *DID* go back and look at the packet captures for these runs (we keep all of our PCAPs) and the traffic was exactly like the other Peer to Peer chatter for GameOver Zeus.

On the top are IP addresses in APNIC countries. Flag test: Japan, Hong Kong, China

On the right are IP addresses in ARIN countries. (Canada, USA)

In the bottom right corner is one LACNIC IP. (Venezuela)

And on the bottom are RIPE countries. (Netherlands, Moldova, Switzerland, Great Britain, Ukraine, Sweden, Belgium, France, and Austria)

The IP addresses on the chart above are also included here in tabular form:

Prominent IP addresses Associated with GameOver Zeus and associated malware

CountryASN#ASN OrganizationIP
CN 4837 CHINA169-BACKBONE CNCGROUP China169 Backbone,CN 221.193.254.122
HK 4515 ERX-STAR PCCW IMSBiz,HK 113.28.179.100
HK 9269 HKBN-AS-AP Hong Kong Broadband Network Ltd.,HK 61.244.150.9
HK 4760 HKTIMS-AP PCCW Limited,HK 218.103.240.27
JP 9365 ITSCOM its communications Inc.,JP 101.111.248.177
JP 45687 MCT-INTERNET Minamikyusyu CableTV Net Inc.,JP 27.54.110.77
JP 38628 WINK-NET HIMEJI CABLE TELEVISION CORPORATION,JP 115.126.143.176
JP 9617 ZAQ KANSAI MULTIMEDIA SERVICE COMPANY,JP 125.4.34.229
CA 577 BACOM - Bell Canada,CA 174.89.110.91
US 36352 AS-COLOCROSSING - ColoCrossing,US 172.245.217.122
US 22773 ASN-CXA-ALL-CCI-22773-RDC - Cox Communications Inc.,US 98.162.170.4
US 7018 ATT-INTERNET4 - AT&T Services, Inc.,US 75.1.220.146
US 7018 ATT-INTERNET4 - AT&T Services, Inc.,US 99.73.173.219
US 33588 BRESNAN-AS - Charter Communications,US 184.166.114.48
US 6128 CABLE-NET-1 - Cablevision Systems Corp.,US 68.197.193.98
US 6128 CABLE-NET-1 - Cablevision Systems Corp.,US 75.99.113.250
US 33490 COMCAST-33490 - Comcast Cable Communications, Inc.,US 67.168.254.65
US 7015 COMCAST-7015 - Comcast Cable Communications Holdings, Inc,US 73.182.194.83
US 6939 HURRICANE - Hurricane Electric, Inc.,US 50.116.4.71
US 8075 MICROSOFT-CORP-MSN-AS-BLOCK - Microsoft Corporation,US 137.116.225.57
US 8075 MICROSOFT-CORP-MSN-AS-BLOCK - Microsoft Corporation,US 137.116.229.40
US 8075 MICROSOFT-CORP-MSN-AS-BLOCK - Microsoft Corporation,US 137.117.197.214
US 8075 MICROSOFT-CORP-MSN-AS-BLOCK - Microsoft Corporation,US 137.117.72.241
US 8075 MICROSOFT-CORP-MSN-AS-BLOCK - Microsoft Corporation,US 137.135.218.230
US 8075 MICROSOFT-CORP-MSN-AS-BLOCK - Microsoft Corporation,US 138.91.18.14
US 8075 MICROSOFT-CORP-MSN-AS-BLOCK - Microsoft Corporation,US 138.91.187.61
US 8075 MICROSOFT-CORP-MSN-AS-BLOCK - Microsoft Corporation,US 138.91.49.30
US 8075 MICROSOFT-CORP-MSN-AS-BLOCK - Microsoft Corporation,US 168.61.80.142
US 8075 MICROSOFT-CORP-MSN-AS-BLOCK - Microsoft Corporation,US 168.61.87.1
US 8075 MICROSOFT-CORP-MSN-AS-BLOCK - Microsoft Corporation,US 168.63.154.114
US 8075 MICROSOFT-CORP-MSN-AS-BLOCK - Microsoft Corporation,US 168.63.211.182
US 8075 MICROSOFT-CORP-MSN-AS-BLOCK - Microsoft Corporation,US 168.63.62.72
US 8075 MICROSOFT-CORP-MSN-AS-BLOCK - Microsoft Corporation,US 23.96.34.43
US 8075 MICROSOFT-CORP-MSN-AS-BLOCK - Microsoft Corporation,US 23.97.133.13
US 8075 MICROSOFT-CORP-MSN-AS-BLOCK - Microsoft Corporation,US 23.98.41.229
US 8075 MICROSOFT-CORP-MSN-AS-BLOCK - Microsoft Corporation,US 23.98.42.224
US 8075 MICROSOFT-CORP-MSN-AS-BLOCK - Microsoft Corporation,US 23.98.64.182
BR 8075 MICROSOFT-CORP-MSN-AS-BLOCK - Microsoft Corporation,US 191.234.43.118
BR 8075 MICROSOFT-CORP-MSN-AS-BLOCK - Microsoft Corporation,US 191.234.52.206
BR 8075 MICROSOFT-CORP-MSN-AS-BLOCK - Microsoft Corporation,US 191.236.85.223
VE 8048 CANTV Servicios, Venezuela,VE 190.37.198.162
AT 8437 UTA-AS Tele2 Telecommunication GmbH,AT 81.189.6.76
BE 5432 BELGACOM-SKYNET-AS BELGACOM S.A.,BE 194.78.138.100
CH 15600 FINECOM Finecom Telecommunications AG,CH 77.239.59.243
FR 16276 OVH OVH SAS,FR 94.23.32.170
GB 2856 BT-UK-AS BTnet UK Regional network,GB 109.153.212.95
GB 2856 BT-UK-AS BTnet UK Regional network,GB 213.120.146.245
GB 2856 BT-UK-AS BTnet UK Regional network,GB 86.159.38.32
MD 31252 STARNET-AS StarNet Moldova,MD 89.28.59.166
NL 1103 SURFNET-NL SURFnet, The Netherlands,NL 130.37.198.100
NL 1103 SURFNET-NL SURFnet, The Netherlands,NL 130.37.198.90
SE 39287 FLATTR-AS Flattr AB,SE 95.215.16.10
UA 13188 BANKINFORM-AS TOV _Bank-Inform_,UA 37.57.41.161
UA 21219 DATAGROUP PRIVATE JOINT STOCK COMPANY _DATAGROUP_,UA 195.114.152.188
UA 42471 FALSTAP-AS OOO TRK Falstap,UA 85.198.156.189
UA 29688 VOSTOKLTD VOSTOK Ltd.,UA 31.42.75.203

Encrypted GameOver Zeus URLs seen by Malcovery

2014-02-06 UK Govt Gateway url::newz24x.com/wp-content/uploads/2014/02/pdf.enc
2014-02-06 UK Govt Gateway url::oilwellme.com/images/banners/pdf.enc
2014-02-06 TNT UK url::newz24x.com/wp-content/uploads/2014/02/pdf.enc
2014-02-06 TNT UK url::oilwellme.com/images/banners/pdf.enc
2014-02-10 UK2fax url::agrimarsystem.pe/images/10UKrh.enc
2014-02-10 UK2fax url::pro-viewer.com/images/10UKrh.enc
2014-02-12 Royal Bank of Scotland url::buzzers.in/media/catalog/category/12UKp.mp3
2014-02-12 Royal Bank of Scotland url::erp.zebronics.com/images/12UKp.mp3
2014-02-18 RingCentral url::iatablet.com/oc-content/uploads/HTML/al1402.pic
2014-02-18 RingCentral url::vietdongatravel.com/image/data/logo/al1402.pic
2014-03-05 Standard Chartered Bank url::broadproductz.zapto.org/ndu/guru/config.bin
2014-03-05 Standard Chartered Bank url::broadproductz.zapto.org/ndu/guru/gate.php
2014-03-06 RingCentral url::thebaymanbook.com/wp-content/uploads/2014/03/al2602.big
2014-03-06 RingCentral url::dominionfoodie.com/images/al2602.big
2014-03-06 Adobe url::cdn.cmatecdnfast.us/os/js/OfferScreen_240_EN.zip
2014-03-06 Adobe url::cdn.cmatecdnfast.us/os/js/OfferScreen_260_EN.zip
2014-03-06 Adobe url::cdn.cmatecdnfast.us/os/OfferScreen_243_FP_spws243.zip
2014-03-06 Adobe url::cdn.eastwhitecoal.us/Advertisers/FlashPlayer_Installer.exe
2014-03-06 Adobe url::downloadupdates.in/MB1/downloadupdate.in/style.css
2014-03-06 Adobe url::downloadupdates.in/MB1/flash_thankyou.php
2014-03-06 French Government url::adultagencyads.com/images/2010/0603UKp.big
2014-03-06 French Government url::trudeausociety.com/images/flash/0603UKp.big
2014-03-18 Citi url::jswcompounding-usa.com/images/TARGT.tp
2014-03-18 Citi url::thesymptomatologynetwork.com/images/TARGT.tp
2014-03-20 BankofAmerica url::lovestogarden.com/images/general/TARGT.tpl
2014-03-20 BankofAmerica url::villaveronica.it/gallery/TARGT.tpl
2014-03-21 Companies House url::fidaintel.com/images/2103UKp.qta
2014-03-21 Companies House url::premiercrufinewine.co.uk/wp-content/uploads/2014/03/2103UKp.qta
2014-03-21 New Fax url::gulf-industrial.com/images/2103USa.qta
2014-03-21 QuickBooks url::bodyfriend.co.uk/images/2103USp.qta
2014-03-21 QuickBooks url::overtonsheepfair.co.uk/wp-content/uploads/2012/06/2103USp.qta
2014-03-27 Banque Populaire url::myeapp.com/wp-content/uploads/2014/03/TARG1.git
2014-03-27 Banque Populaire url::ramirezcr.com/images/TARG1.git
2014-03-27 HSBC url::knockoutsecrets.com/wp-content/uploads/2014/03/2703UKc.git
2014-03-27 HSBC url::vequi.com/images/2703UKc.git
2014-03-28 Sky url::hardmoneylenderslosangeles.com/abc/2803UKd.wer
2014-03-28 Sky url::igsoa.net/Book/2803UKd.wer
2014-03-28 Sage url::hardmoneylenderslosangeles.com/abc/2803UKd.wer
2014-03-28 Sage url::igsoa.net/Book/2803UKd.wer
2014-03-31 Voicemail Message url::albergolarese.com/css/3103UKm.rih
2014-03-31 Voicemail Message url::direttauto.com/scripts/3103UKm.rih
2014-03-31 Lloyds Bank url::bormanns-wetter.de/scripts/3103UKd.rih
2014-03-31 Lloyds Bank url::brucewhite.org/images/3103UKd.rih
2014-04-01 RingCentral url::atlantafloorinstallation.com/wp-content/plugins/akismet/index.zpi
2014-04-01 RingCentral url::ayat.onlinewebshop.net/img/index.zpi
2014-04-01 Royal Bank of Scotland url::miss-loly.com/Scripts/0104UKd.bis
2014-04-01 Royal Bank of Scotland url::photovolt.ro/script/0104UKd.bis
2014-04-01 eFax url::apacsolutions.com/test/Targ-0104USr.bis
2014-04-01 eFax url::cfklc.com/downloads/Targ-0104USr.bis
2014-04-01 Wells Fargo url::all-products.biz/css/Targ-0104USd.bis
2014-04-01 Wells Fargo url::smokeylegend.com/css/Targ-0104USd.bis
2014-04-01 Xerox url::atifmalikmd.org/css/Targ-0104USm.bis
2014-04-01 Xerox url::contactdbinc.com/css/Targ-0104USm.bis
2014-04-07 New Fax url::abwidiyantoro.com/images/0804UKm.jpi
2014-04-07 New Fax url::kworldgroup.com/css/0804UKc.jpi
2014-04-07 New Fax url::rainda.com/css/0804UKc.jpi
2014-04-07 New Fax url::robertcairns.co.uk/wp-content/uploads/2014/04/0804UKm.jpi
2014-04-07 NY Dept of Taxation and Finance url::gisticinc.com/wp-content/uploads/2014/04/0804UKr.jpi
2014-04-07 NY Dept of Taxation and Finance url::vtiger.gisticinc.com/test/logo/0804UKr.jpi
2014-04-08 Swiftpage, Inc url::isapport.com/Images/n0804UKm.dim
2014-04-08 Swiftpage, Inc url::metek-mkt.com/images/scripts/n0804UKm.dim
2014-04-09 HSBC url::musicbanda.com/css/0904UKd.rar
2014-04-09 HSBC url::sunsing.com.sg/images/0904UKd.rar
2014-04-09 New Fax url::renaissancepmc.com/scripts/0904US.rar
2014-04-09 New Fax url::thegrandbasant.com/img/icons/0904US.rar
2014-04-10 Xerox url::ebazari.com/uploads/brands/Targ-1004USr.enc
2014-04-10 Xerox url::rollonskips.com/images/banners/Targ-1004USr.enc
2014-04-14 Santander url::vv-international.eu/food/1404UKd.rar
2014-04-17 PayPal url::artncraftemporio.com/media/css/1704UKd.rar
2014-04-17 PayPal url::hrprovider.com/img/img/1704UKd.rar
2014-04-17 PayPal url::artncraftemporio.com/media/css/1704UKd.rar
2014-04-17 PayPal url::hrprovider.com/img/img/1704UKd.rar
2014-04-17 IRS url::fergieandco.org/wp-content/uploads/2014/03/Targ-1704USd.rar
2014-04-17 IRS url::newsilike.in/wp-content/lbp-css/black/Targ-1704USd.rar
2014-04-23 Royal Bank of Scotland url::aoneteleshop.com/images/payments/s2304UKd.rar
2014-04-23 Royal Bank of Scotland url::czargroup.net/wp-content/uploads/2014/04/s2304UKd.rar
2014-04-23 Companies House url::aoneteleshop.com/images/payments/s2304UKd.rar
2014-04-23 Companies House url::www.czargroup.net/wp-content/uploads/2014/04/s2304UKd.rar
2014-04-24 Generic Voicemail url::dotspiders.sg/test/clocks/2404UKs.tar
2014-04-24 Generic Voicemail url::mc-saferentals.com/images/2404UKs.tar
2014-04-25 Unity Messaging System url::altpowerpro.com/images/stories/highslide/Targ-2404USm.tar
2014-04-25 Unity Messaging System url::tmupi.com/media/images/icons/team/Targ-2404USm.tar
2014-04-29 Citi url::capsnregalia.com/download/2904UKpm.zip
2014-04-29 Citi url::perfumeriaamalia.com/images/stories/2904UKpm.zip
2014-04-30 UK Gov't Gateway url::factoryrush.com/boxbeat/uploads/3004UKdp.tar
2014-04-30 UK Gov't Gateway url::vestury.com/js/fckeditor/editor/js/3004UKdp.tar
2014-04-30 Sky url::factoryrush.com/boxbeat/uploads/3004UKdp.tar
2014-04-30 Sky url::vestury.com/js/fckeditor/editor/js/3004UKdp.tar
2014-04-30 IRS url::capsnregalia.com/download/scripts/Targ-3004USmp.tar
2014-04-30 IRS url::worldbuy.biz/scripts/Targ-3004USmw.tar
2014-05-05 Microsoft url::iknowstudio.com/scripts/0505USdw.dat
2014-05-05 Microsoft url::luxesydiseno.com/images/stories/brands/0505USdw.dat
2014-05-06 BT.com url::BIZ-VENTURES.NET/scripts/0605UKdp.rar
2014-05-06 BT.com url::realtech-international.com/css/0605UKdp.rar
2014-05-06 HMRC url::BIZ-VENTURES.NET/scripts/0605UKdp.rar
2014-05-06 HMRC url::realtech-international.com/css/0605UKdp.rar
2014-05-06 Generic Voicemail url::oligroupbd.com/images/Targ-0605USmw.enc
2014-05-06 Generic Voicemail url::touchegolf.com/css/Targ-0605USmw.enc
2014-05-06 US Postal Service url::eirtel.ci/images/0605USdw.enc
2014-05-06 US Postal Service url::smartsolutions.ly/css/0605USdw.enc
2014-05-07 Bank of America url::addcomputers.com/downloads/Targ-0705USmw.enc
2014-05-07 Bank of America url::mindinstitute.ro/images/Targ-0705USmw.enc
2014-05-07 NYC Govt url::addcomputers.com/downloads/Targ-0705USmw.enc
2014-05-07 NYC Govt url::mindinstitute.ro/images/Targ-0705USmw.enc
2014-05-07 BT.com url::k-m-a.org.uk/images/jquerytree/0705USmp.enc
2014-05-07 BT.com url::tuckerspride.com/wp-content/uploads/2014/05/0705USmp.enc
2014-05-07 NatWest url::bumisaing.com/wpimages/wpThumbnails/0705UKmp.zip
2014-05-07 NatWest url::generation.com.pk/flash/0705UKmp.zip
2014-05-07 Swiftpage url::bumisaing.com/wpimages/wpThumbnails/0705UKmp.zip
2014-05-07 Swiftpage url::generation.com.pk/flash/0705UKmp.zip
2014-05-07 Swiftpage url::bumisaing.com/wpimages/wpThumbnails/0705UKmp.zip
2014-05-07 Swiftpage url::generation.com.pk/flash/0705UKmp.zip
2014-05-07 QuickBooks url::k-m-a.org.uk/images/jquerytree/0705USmp.enc
2014-05-07 QuickBooks url::tuckerspride.com/wp-content/uploads/2014/05/0705USmp.enc
2014-05-08 Companies House url::accessdi.com/wp-content/uploads/2014/05/0805UKdp.dat
2014-05-08 Companies House url::mpharmhb.com/images/banners/0805UKdp.dat
2014-05-08 Paychex url::localalarmbids.com/wp-content/uploads/2012/12/0805USmp.rar
2014-05-08 Paychex url::pharmaholic.com/images/banners/0805USmp.rar
2014-05-12 NatWest url::plvan.com/css/1205UKdm.tar
2014-05-12 NatWest url::srhhealthfoods.com/test/1205UKdm.tar
2014-05-12 ADP url::datanethosting.com/css/Targ-1205USmp.enc
2014-05-12 ADP url::distrioficinas.com/fonts/Targ-1205USmp.enc
2014-05-12 Royal Bank of Scotland url::plvan.com/css/1205UKdm.tar
2014-05-12 Royal Bank of Scotland url::srhhealthfoods.com/test/1205UKdm.tar
2014-05-13 IRS url::consumerfed.net/css/1305UKmw.zip
2014-05-13 IRS url::irishtroutflies.ie/images/1305UKmw.zip
2014-05-13 NYC Govt url::loquay.com/css/1305UKdp.zip
2014-05-13 NYC Govt url::moraza.com.my/images/1305UKdp.zip
2014-05-13 Xerox url::loquay.com/css/1305UKdp.zip
2014-05-13 Xerox url::moraza.com.my/images/1305UKdp.zip
2014-05-13 NatWest url::luxesydiseno.com/images/powerslide/Concha/1305UKdw.zip
2014-05-13 NatWest url::paulaggg.com/css/1305UKdw.zip
2014-05-14 Microsoft url::djdawson.com/css/1405UKdw.enc
2014-05-14 Microsoft url::elpenterprisesinc.com/wp-content/uploads/2014/05/1405UKdw.enc
2014-05-14 Sage url::ballroom-intergalactica.com/wp-content/themes/twentythirteen/css/1405UKdp.enc
2014-05-14 Sage url::indoorea.com/webfiles/css/1405UKdp.enc
2014-05-14 Intuit url::martabrixton.com/css/Targ-rhc1405.dat
2014-05-14 Intuit url::mindinstitute.ro/Web3/Upload/Targ-rhc1405.dat
2014-05-14 NatWest url::jessicahann.co.uk/wp-content/uploads/2013/13/1405UKmp.enc
2014-05-14 NatWest url::mortgagebidders.ca/fonts/1405UKmp.enc
2014-05-14 ADP url::martabrixton.com/css/Targ-rhc1405.dat
2014-05-14 ADP url::mindinstitute.ro/Web3/Upload/Targ-rhc1405.dat
2014-05-15 eFax url::factoryrush.com/test/1505UKmp.zip
2014-05-15 eFax url::techwin.com.pk/css/1505UKmp.zip
2014-05-15 UK Ministry of Justice url::floworldonline.com/wp-content/uploads/2014/04/1505UKdp.zip
2014-05-15 UK Ministry of Justice url::sugarlandrx.com/media/css/1505UKdp.zip
2014-05-15 eFax url::dubaimovers.info/scripts/Targ-1505USdp.tar
2014-05-15 eFax url::entrepreneurindia.com/css/Targ-1505USdp.tar
2014-05-15 eFax url::www.entrepreneurindia.com/css/Targ-1505USdp.tar
2014-05-15 Fidelity url::dubaimovers.info/scripts/Targ-1505USdp.tar
2014-05-15 Fidelity url::entrepreneurindia.com/css/Targ-1505USdp.tar
2014-05-15 Fidelity url::www.entrepreneurindia.com/css/Targ-1505USdp.tar
2014-05-15 Dun & Bradstreet url::dubaimovers.info/scripts/Targ-1505USdp.tar
2014-05-15 Dun & Bradstreet url::entrepreneurindia.com/css/Targ-1505USdp.tar
2014-05-15 Dun & Bradstreet url::www.entrepreneurindia.com/css/Targ-1505USdp.tar
2014-05-16 Bank of America url::gmdf.net/js/Targ-1605USdw.tar
2014-05-16 Bank of America url::kuukaarr01.com/wp-content/uploads/2014/05/Targ-1605USdp.tar
2014-05-16 Bank of America url::kuukaarr02.com/wp-content/uploads/2014/05/Targ-1605USdw.tar
2014-05-16 Bank of America url::malkanat.com/images/Targ-1605USdp.tar
2014-05-16 Bank of America https://dl.dropboxusercontent.com/s/vfoim5op006sjdv/SecureMessage.zip
2014-05-16 Bank of America https://dl.dropboxusercontent.com/s/xn26h1fppik5np6/BankofAmerica.scr
2014-05-19 Santander url::aanchalgroup.com/wp-content/uploads/2013/09/1905UKdp.zip
2014-05-19 Santander url::albus-capital.com/css/1905UKdp.zip
2014-05-19 Santander url::paperonotel.com/Scripts/heap170id2.exe
2014-05-19 Wells Fargo url::mersinprefabrik.com/Css/1905USmw.dct
2014-05-19 Wells Fargo url::paperonotel.com/Scripts/heap170id2.exe
2014-05-19 Wells Fargo url::seminarserver.com/css/1905USmw.dct
2014-05-20 HSBC url::lospomos.org/images/button/2005UKmw.zip
2014-05-20 HSBC url::task-team.com/css/2005UKmw.zip
2014-05-20 NYC Govt url::lospomos.org/images/button/2005USmw.zip
2014-05-20 NYC Govt url::task-team.com/css/2005USmw.zip
2014-05-20 UPS url::auracinematics.com/christine/Christine/2005USdp.zip
2014-05-20 UPS url::protecca.com/fonts/2005USdp.zip
2014-05-20 UPS url::alamx.com/images/RCH2005.zip
2014-05-20 UPS url::evedbonline.com/images/RCH2005.zip
2014-05-20 Royal Bank of Scotland url::lospomos.org/images/button/2005UKmw.zip
2014-05-20 Royal Bank of Scotland url::task-team.com/css/2005UKmw.zip
2014-05-20 LexisNexis url::alamx.com/images/RCH2005.zip
2014-05-20 LexisNexis url::evedbonline.com/images/RCH2005.zip
2014-05-21 Credit Agricole url::eleanormcm.com/css/2105UKdp.rar
2014-05-21 Credit Agricole url::frizou.org/06-images/2105UKdp.rar
2014-05-21 Credit Agricole url::paperonotel.com/Scripts/heap170id2.exe
2014-05-21 HSBC url::cedargrill.sg/css/2105UKdw.rar
2014-05-21 HSBC url::chezalexye.com/css/2105UKdw.rar
2014-05-21 JP Morgan url::footballmerch.com/media/css/Targ-2105USmw.tar
2014-05-21 JP Morgan url::myacoub.com/wp-content/uploads/2014/05/Targ-2105USmw.tar
2014-05-27 Hewlett-Packard url::flutterhost.com/demo/2705UKdp.rar
2014-05-27 Hewlett-Packard url::lotwatch.net/images/2705UKdp.rar
2014-05-27 Xerox url::auracinematics.com/acc/b02.exe
2014-05-27 Xerox url::feelhomely.com/beta/eshopbox/2705USmp.opt
2014-05-27 Xerox url::the-dunn.com/css/2705USmp.opt
2014-05-27 Xerox url::auracinematics.com/acc/b02.exe
2014-05-27 Xerox url::feelhomely.com/beta/eshopbox/2705USmp.opt
2014-05-27 Xerox url::the-dunn.com/css/2705USmp.opt
2014-05-29 Visa url::homerenov.org/wp-content/uploads/2014/05/Targ-2905USmp.tar
2014-05-29 Visa url::qadindunyasi.az/images/Targ-2905USmp.tar
2014-05-30 Sky url::3dparsian.com/images/banners/3005UKdp.rar
2014-05-30 Sky url::kuukaarr01.com/wp-content/themes/twentytwelve/css/3005UKdp.rar
2014-05-30 Sky url::utraconindia.com/images/social/heapid2.exe
2014-05-30 HSBC url::bag-t.com/css/3005UKmw.rar
2014-05-30 HSBC url::seminarserver.com/html/3005UKmw.rar

Monday, June 02, 2014

Is the Game Over for GameOver Zeus?

Several weeks ago law enforcement friends in Pittsburgh started asking people not to publish anything too public about GameOver Zeus. When we asked why, we got a teasing "You'll see!" Now our ISP friends that were participating in the effort are grinning ear to ear as we may actually have a chance to disrupt Zeus in a meaningful way. Being a legal geek, I was excited to have the documents published on the main Justice website today at www.justice.gov/opa/gameover-zeus.html.

The Complaint against Evgeniy Mikhailovich Bogachev aka Slavik, aka Pollingsoon was unsealed in court where the Pittsburgh FBI led the investigation into CryptoLocker and GameOver Zeus. In addition to Bogachev, charges are filed against several aliases of as-yet-unidentified hackers, "Temp Special", "Ded", Chingiz (aka Chingiz 911), and Mr.KyKyPyKy. The Complaint charges that "Together, GOZ and Cryptolocker have infected hundreds of thousands of computers around the world and have generated losses that exceed $100 million."

Some of the specific cases mentioned in the complaint include:

  • A composite materials company in the Western District of Pennsylvania which lost more than $198,000 from its bank account using credentials stolen by the Defendants through the use of GOZ; (The Pittsburgh Indictment shares more details, telling us this was Haysite Reinforced Plastics, whose PNC Bank account was fraudulently accessed and used to send their money to a Mule account in the name of Lynch Enterprises, LLC, at SunTrust Bank in Atlanta, Georgia, after they clicked on a NACHA email informing them their ACH payment had failed, in October 2011. They also transfered $175,756.91 to an account belonging to R&R Jewelers, and ATTEMPTED six additional transfers, all on October 20, 2011. The money in the SunTrust account was quickly moved on ($99,822 of it, anyway) to an HSBC account in London.)
  • An Indian tribe in Washington - $277,000
  • A corporation managing assisted living facilities in Pennsylvania - $190,800
  • A regional bank in Northern Florida - $7 Million
CryptoLocker is described separately as having "first emerged in mid-to-late 2013" and infected "more than 230,000 computers, including more than $120,000 in the United States.

Just between October 15, 2013 and December 18, 2013, we know that $27 million in ransom payments were made, just by tracking the ransom payments made using Bitcoin!

The charges in the criminal complaint are:

Count I: Wire fraud: 18 USC Section 1343 "Having devised a scheme or artifice to defraud and for obtaining money by means of false or fraudulent pretenses and transmitting and causing to be transmitted by means of wire communications in interstate and foreign commerce, writings, signs, and signals for the purpose of executing such scheme or artifice.

Count II: Bank Fraud: 18 USC Section 1344 "knowingly executing a scheme or artifice to defraud financial institutions insured by the FDIC and to obtain moneys under the custody and control of these institutions by means of false and fraudulent pretenses and representations.

Count III: Unauthorized interception of electronic communications: 18 USC Section 2511 "intentionally intercepting electronic communications, and intentionally using and endeavoring to use the contents of the electronic communications knowing that the information is obtained through the unauthorized interception of electronic communications."

all of which, according to 18 USC Section 1345(a) and (b) allows Injunctive Relief to prevent a continuing and substantial injury to the owners and legitimate users of the infected computers.

An FBI Pittsburgh cyber agent was the affiant in the 28 page Application for Temporary Restraining Order recounts that while the largest known single wire transfer was a $6.9 million wire, fraudulent wires in the amount of $1 million dollars were "very common." A single bank experienced 11 fraudulent wires, with six being for more than $950,000 and the largest being 2 million dollars!

The GOZ affidavit mentions a few email addresses, Bogachev uses as one email address, bollinger.evgeniy@yandex.ru, while Chingiz 911 uses charajiang16@gmail.com. Seeing the nickname "Ded" as one of the members of the gang, I can't help but recall "Ded Pixto" the nickname for Stanislav Avdeiko the Koobface malware author.

So how will this "takedown" actually work? First, some hard work by a couple genius malware reverse engineers at Dell Secure Works and CrowdStrike helped the Pittsburgh FBI agent to understand the current Command & Control infrastructure so it could be rendered harmless. The problem though, is that both GOZ and Cryptolocker have a built-in backup plan in the form of a Domain Generation Algorithm. The job of a DGA is to allow the botmaster to IN THE FUTURE reconnect to his bots using infrastructure that neither the bots nor the botmaster have even created yet. A formula is used to calculate a domain name based on a timestamp. So, if NONE of the hard-coded IP addresses are able to be reached, the bot will look up the current date and begin "guessing" domains that the criminal may have registered for use to update the bot with new hard-coded addresses. As a few examples, on July 1, 2014, CryptoLocker will try to connect to 1,000 domains, including:

wncbbejfurrw.net
kbdnkmpgxlxh.biz
aevmpupnouqy.ru
nrwyydvorowj.org
bvgurlkgcwya.co.uk
ojhhbtqhfqfk.info
eqcoayuicfrp.com
fsdnbhyofoiv.net
fimwcppbphaq.biz
gknvdxthsqqw.ru
iygiqgvjjkys.org
jbhhroapmtpy.co.uk
jqqqswqcwmht.info
ksrptfuiavxa.com
klrmfgyihrch.net
xysyolodvgen.biz
mgcjywthscyu.ru
atdvicjchqbb.org
otvgvnajowjk.co.uk
The Temporary Restraining Order (TRO) seeks an Order that:

1) directs four U.S. based internet domain Registries to block access to around 900 PAGES of domain names seemingly the "future" list of DGA-generated domain names for CryptoLocker and GOZ. The GameOver Zeus domains are listed in Appendix A while the CryptoLocker domains are listed in Appendix B. Because ICANN only has jurisdiction over the Generic TLDs, this approach doesn't work for the ".ru" domains. CryptoLocker also uses ".co.uk" domains, so one would hope that the British government has asked for a similar favor from their counterpart registries. The four Registries in the US were, VeriSign, Inc., representing .com and .net, Neustar, Inc., representing .biz, Affilias USA, Inc., representing .info, and Public Interest Registry, representing .org.

Appendix A actually contains 25,937 domains for Game Over Zeus, arranged in ten columns, with three columns of domains listed on pages 1-69, 70-138, 139-207, and then a single column on pages 208 to 276. Its actually seven columns of 2594 domains and three columns of 2593 domains or 25,937 domains for Game Over Zeus.

Appendix B has six columns on pp. 1-176, pp.177-352, and then six columns of various length from 353 to the end of the 704 page document, for a total of 130,421 domains for CryptoLocker.

Affilias, Neustar, Verisign, and Public Interest Registry are ordered to redirect all of those 156,000 or so domains to use the nameservers ns1.kratosdns.net and ns2.kratosdns.net, preventing the criminals from using those domains to re-establish control of their botnet.

2) directs the twenty largest ISPs in America to not allow access from their networks to the .RU domains that the DGA can make, as the .RU domains are not under ICANN control. The ISPs named here are:

Cablevision, AT&T, Cox, Comcast, Mediacom, AOL, Frontier, Sprint, Time Warner Cable, Verizon, Charter, CenturyLink, Suddenlink, Wide Open West, Windstream, Level 3, Armstrong Group of Companies, Bright House, Earthlink, and NTT America.

Those ISPs are forbidden to allow traffic to the .ru domains listed in Appendix C.

3) To redirect all traffic intended for one of those domains to .gov controlled servers

and

4) to seek a Pen Register/Trap and Trace Order that would gather information about the nodes directed to those replacement boxes, and to share that information back to the ISPs and victims to help protect themselves. This "Dialing, Routing, Addressing, and Signaling" data (called DRAS in telephone-legalese) is to be turned over to the government so that attempts can be made to clean up these victims computers.

In cooperation with these efforts, McAfee is providing their "Stinger" program to be used by any victims to clean and remove GameOver Zeus or CryptoLocker infections.

All of that is now in play ... it is too early to tell if the game is really over, but best of luck and congratulations to the fine agents and CCIPS lawyers who made this possible!